Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What HashiCorp states |
|---|---|
License | Terraform core, the command line interface and graph engine, is source-available under the Business Source License 1.1. |
Providers | Plugins that Terraform can download automatically from the Terraform Registry. HashiCorp develops some; other organizations develop others. |
Ways to buy HCP | Pay-as-You-Go: on-demand, usage-based billing with no long-term commitment. Flex: single and multi-year plans with preferred pricing, through sales. Enterprise Self Managed: fully customizable plans for maximum control. |
Learning and certification | Documentation, tutorials on HashiCorp's learning platform, the HashiCorp Discuss forum and the HashiCorp Certified: Terraform Associate exam. |
Our take
Choose Terraform when one declarative workflow should provision your cloud, private datacenter, network and SaaS infrastructure, and every change should be reviewed as a plan before it runs. Pick HCP Terraform if you would rather not operate the tooling yourself, since HashiCorp Cloud Platform delivers its products as a managed service. Pick Terraform Enterprise if security, compliance or operational rules require you to self-manage.
Evaluate Terraform
Comparisons
Where it stands out
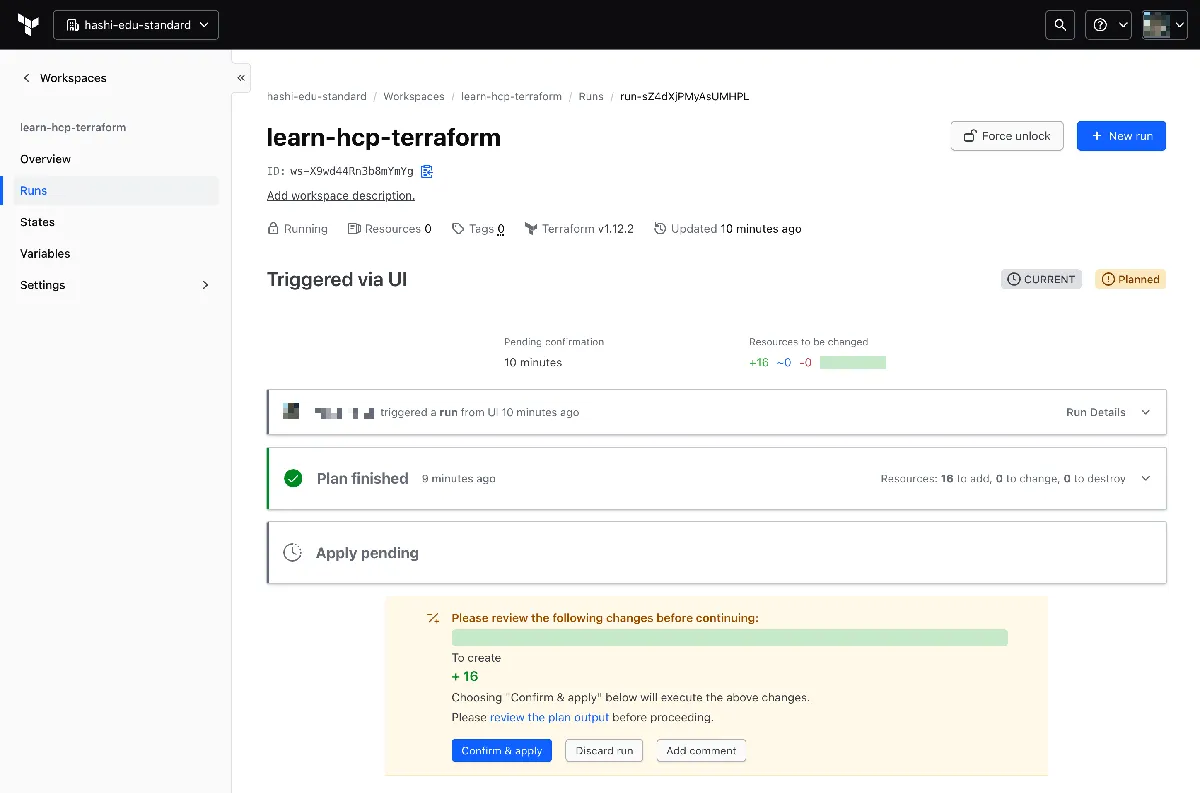
You see changes before they happen. Terraform generates an execution plan that shows what it will do when you apply. It builds a graph of your resources, changes independent resources in parallel and shows dependencies, so complex changesets can run with little manual work.
One workflow for many kinds of infrastructure. HashiCorp positions Terraform as a single workflow for cloud, private datacenter and SaaS infrastructure, with codified network templates. It can manage popular service providers as well as custom in-house systems.
Guardrails for platform teams. HashiCorp lists VCS integration for CI/CD, reusable modules, policy as code, drift detection with continuous validation, and automatic clean-up of temporary resources. HCP Terraform Standard and Premium customers also get Infragraph, a live view of infrastructure across the estate, which HashiCorp labels as limited availability and public preview.
Shared team workflow in HCP Terraform. HashiCorp's pricing page compares HCP Terraform editions on features such as remote state storage, VCS connection, projects, secure variable storage, remote runs (plan & apply), a private registry and team management. These move state, runs and modules out of individual laptops and into one shared place.
Product screenshot
Trade-offs to weigh
Check who maintains each provider. Your experience with a given service depends on that provider's maintainer, so review the providers you rely on before you standardize on them.
The bill follows your resource count, not your headcount. Each resource Terraform manages in a paid HCP Terraform edition adds to the monthly bill, so a large estate of small resources can cost more than its number of servers suggests. Confirm the rate for your resource count before you commit.
Pricing and plan conditions
Paid HCP Terraform editions list a starting monthly price per resource, rated hourly. HashiCorp offers a $500 credit to get started, usable across the IBM HashiCorp Cloud Platform. All displayed prices are in US dollars, for eligible business customers only, and exclude applicable country taxes or fees. HashiCorp's Terraform product page also describes an HCP Terraform Free tier with up to 500 managed resources, unlimited users and apply cycles, and essential security features such as SSO and policy as code.
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Edition | Published price | Delivery, fit and inclusions |
|---|---|---|
IBM HCP Terraform Essentials | Starting at $0.10 per month per resource, rated hourly at $0.00013 per hour | Cloud. For professional individuals or teams adopting infrastructure as code provisioning. |
IBM HCP Terraform Standard | Starting at $0.47 per month per resource, rated hourly at $0.00064 per hour | Cloud. For enterprises standardizing and managing infrastructure automation and lifecycle. Includes HCP Waypoint. |
IBM HCP Terraform Premium | Starting at $0.99 per month per resource, rated hourly at $0.00135 per hour | Cloud. For enterprises that want a secure, self-service workflow. Includes HCP Waypoint. |
IBM HCP Terraform Europe | Custom Pricing | Cloud, with geographic service locality in Europe for security, compliance and operations needs. Includes HCP Waypoint Europe. |
IBM Terraform Enterprise | Custom Pricing | Self-managed, for enterprises with security, compliance and operational needs. Premium support included. |
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
370 GitHub commits 90d50.2k GitHub stars0 vulnerabilities across 1 package
See all signals from 7 sources
npm · cdktf@0.21.0
Alternatives to Terraform
The reviewed substitutes for Terraform among the infrastructure as code, and what would make each one the better answer.
Direct alternatives
Reviewed substitutes: products bought for the same job, where a team picks one.
- OpenTofu
- OpenTofu is a fork of Terraform, created in 2023 after HashiCorp moved Terraform to the Business Source Licence, and now a Linux Foundation project under MPL-2.0. It reads the same HCL and consumes the same provider ecosystem, so the two are as directly substitutable as any pair in this catalogue, and a team runs one. The decision is licence and governance rather than capability: an OSI-approved licence with a public steering committee against a single vendor's supported stack.Applies to: Declaring and reconciling cloud infrastructure in HCL. OpenTofu stands in for Terraform when the Business Source Licence is a problem for your organisation, or when open governance of a core dependency is worth a migration; Terraform stands in when the licence poses no issue and its commercial stack and larger body of documentation decide.
Other approaches
A different approach to the same problem. Each substitutes only for the workload named beside it.
- Pulumi
- The same job with a different authoring model. Terraform constrains infrastructure to HCL, which is what makes a plan diff predictable to a reviewer; Pulumi expresses it in TypeScript, Python, Go or .NET, so loops, tests, type checking and package managers come from the language. Conditional because the right answer follows from who maintains the code: a full programming language buys abstraction and testing at the cost of the constraint that makes review easy.Applies to: Declaring cloud infrastructure as code. Pulumi stands in for Terraform when the people writing infrastructure are programmers who want their own language and tooling, or when reusable components should ship through npm and PyPI; Terraform stands in when a constrained configuration language suits the reviewers, or the estate is already written in HCL.
Related technologies
Normally used together rather than chosen between, so these are not alternatives.
- Kubernetes
- Open-source container orchestration platform for automating deployment and scalingApplies to: Whether infrastructure provisioning and container runtime are the same job.
- Docker
- Docker is a platform designed to help developers build, share, and run container applications. We handle the tedious setup, so you can focus on the code.Applies to: Whether infrastructure provisioning and container runtime are the same job.
Head to head
See detailed alternatives analysis
If you are evaluating Terraform alternatives, you are likely reconsidering your infrastructure-as-code strategy after IBM's acquisition of HashiCorp, the BSLv2 license change, or the shift to the Resources Under Management (RUM) pricing model. Terraform remains one of the most widely used IaC tools with a mature provider ecosystem, but the landscape has shifted enough that teams should understand their options. Below we examine the developer tools most commonly compared to Terraform and help you determine which path fits your infrastructure needs.
Top Alternatives Overview
The alternatives listed here span different layers of the infrastructure and developer tooling stack. Kubernetes is an open-source container orchestration platform that complements or partially overlaps with Terraform when managing cloud-native workloads. While Terraform provisions the underlying infrastructure, Kubernetes manages containerized applications running on top of it. Many teams use both together, but Kubernetes-native tools like Helm and Kustomize can replace Terraform for cluster-internal resource management.
Docker provides the containerization layer that packages applications into portable units. Docker itself is not an IaC tool, but Docker Compose and the extensive container ecosystem offer declarative configuration approaches that overlap with Terraform for application-level infrastructure. Teams heavily invested in containerized workflows may find Docker's tooling sufficient for local and staging environments.
Retool is a low-code platform for building internal tools, connecting to databases and APIs with drag-and-drop components. Budibase offers similar capabilities starting at $19/month for Pro. Appsmith provides a free self-hosted option with cloud plans from $15/month. Streamlit is an open-source Python framework for data apps. These platforms serve a different purpose from Terraform -- they build application interfaces rather than provision infrastructure. Cursor is an AI-powered code editor and Dash is a Python visualization framework, neither of which functions as an IaC replacement.
For teams specifically seeking a direct Terraform replacement for infrastructure provisioning, the most relevant tools to evaluate from this list are Kubernetes (for cluster-native resource management) and Docker (for container-centric workflows), while recognizing that dedicated IaC alternatives like OpenTofu, Pulumi, and AWS CloudFormation exist outside this comparison set.
Architecture and Approach Comparison
Terraform uses HashiCorp Configuration Language (HCL), a declarative domain-specific language, to define infrastructure resources across cloud providers. It maintains a state file that tracks the current state of provisioned resources and calculates a plan to reconcile desired state with actual state. Terraform's provider model supports hundreds of cloud services and SaaS products through a plugin architecture. The tool is written in Go, and its broad adoption is reflected in its active GitHub presence and community contributions.
Kubernetes takes a fundamentally different architectural approach. Rather than provisioning cloud resources, it orchestrates containers using YAML manifests that declare desired workload states. The Kubernetes control plane continuously reconciles actual state with desired state, similar in philosophy to Terraform but operating at the container layer. As a CNCF graduated project, Kubernetes is one of the most actively maintained open-source projects in the infrastructure space, with features including service discovery, load balancing, storage orchestration, automated rollouts and rollbacks, and self-healing capabilities.
Docker operates at the application packaging layer. Its architecture centers on building container images from Dockerfiles and running them via the Docker engine. Docker Compose extends this with multi-service YAML definitions for orchestrating multiple containers on a single host. The key architectural distinction is scope: Terraform manages cloud resources (VMs, networks, databases), Kubernetes manages containers and services at scale, and Docker manages individual container images and local development environments.
Retool, Budibase, Appsmith, and similar low-code platforms use a browser-based visual builder architecture with pre-built components that connect to databases and APIs. They operate at the application layer and have no overlap with infrastructure provisioning workflows. Appsmith stands out as fully open-source and self-hostable, while Retool offers the most mature enterprise feature set.
Pricing Comparison
Terraform's open-source CLI remains free. HCP Terraform (the managed SaaS product, formerly Terraform Cloud) uses a Resources Under Management (RUM) pricing model introduced in June 2023. The current tiers include a Free plan with up to 500 managed resources, an Essentials tier at approximately $0.10 per managed resource per month, a Standard tier at approximately $0.47 per managed resource per month, and a Premium tier at approximately $0.99 per managed resource per month. Resources are billed hourly based on peak hourly usage, with partial hours counted as full hours. IBM also offers a $500 trial credit for new paid accounts. IBM Terraform Enterprise (the self-hosted option) is sold separately.
Kubernetes is fully open source under the Apache 2.0 license with no commercial tiers from the project itself. Infrastructure costs come from the cloud provider running the cluster (EKS, GKE, AKS) or from self-hosting on bare metal.
Docker offers a Personal tier at no cost, with paid tiers scaling upward for Pro, Team, and Business needs. The Docker engine and CLI tools remain open source under Apache 2.0.
Among the low-code alternatives, Retool offers a Free tier for up to 5 users with paid plans starting at $75 per user per month. Budibase starts at $19/month for Pro, $49/month for Premium, and $299/month for Business. Appsmith provides a free self-hosted option with cloud plans at $15/month and an enterprise tier at $2,500/month.
The critical pricing consideration for Terraform specifically is the RUM model's unpredictability. Because every managed resource (including individual security group rules and IAM policies) counts toward billing, costs can scale rapidly with complex infrastructure. Even at the lowest paid tier, costs grow linearly with every resource added, and common infrastructure objects like individual security group rules each count as a separate managed resource. Teams managing thousands of resources should model their projected costs carefully before committing to HCP Terraform.
When to Consider Switching
Consider moving away from HCP Terraform if the RUM pricing model creates unpredictable monthly bills for your infrastructure scale. Organizations managing large numbers of fine-grained resources (security group rules, IAM policies, S3 lifecycle rules) are most affected, as each individual resource counts toward billing regardless of its complexity or cost.
The BSLv2 license change in August 2023 is another catalyst. If your organization requires a fully open-source IaC tool with no license restrictions on commercial use, evaluate OpenTofu, the community fork that maintains the Mozilla Public License. For teams already managing Kubernetes-native workloads extensively, reducing the Terraform footprint in favor of Kubernetes-native tools like Crossplane or Helm for in-cluster resource management can simplify the toolchain.
Teams that primarily use a single cloud provider should also consider whether the provider's native IaC tool (AWS CloudFormation, Azure Bicep, Google Cloud Deployment Manager) offers sufficient coverage. Provider-native tools eliminate the state management overhead that Terraform requires and often integrate more tightly with the provider's console and CI/CD features.
However, if your infrastructure spans multiple cloud providers and on-premises environments, Terraform's multi-cloud provider ecosystem remains its strongest advantage, and few alternatives match its breadth. We recommend staying with Terraform (or moving to OpenTofu) in multi-cloud scenarios unless your team has specific licensing or pricing constraints that force a change.
Migration Considerations
Migrating away from Terraform requires careful state management planning. Terraform state files contain the mapping between your HCL definitions and actual cloud resources. Any migration path must account for this state, either by importing resources into the target tool's state management system or by running both tools in parallel during a transition period. Use terraform state list and terraform state show to build a complete inventory before making any changes.
For teams moving to OpenTofu, the migration is relatively straightforward since OpenTofu forked from Terraform 1.5.x and maintains compatibility with existing HCL configurations and state files. You can often switch by replacing the terraform binary with tofu and running initialization commands. However, feature divergence between the projects will increase over time, so evaluate whether OpenTofu supports the providers and modules your configurations depend on.
Migrating to Kubernetes-native tooling like Crossplane involves a larger architectural shift. You would need to redefine cloud resources as Kubernetes Custom Resources rather than HCL, which means rewriting configurations rather than converting them. This approach works best when adopted incrementally, starting with new resources rather than attempting to migrate an entire existing Terraform codebase.
For provider-native tools, most cloud providers offer import commands that can bring existing resources under their management. AWS CloudFormation's resource import, for example, lets you adopt resources that Terraform currently manages. The process typically involves removing the resource from Terraform state, importing it into the new tool, and verifying that the new tool's drift detection confirms alignment.
Regardless of the target, we recommend running both tools in parallel for a transition period, maintaining Terraform in read-only mode while the replacement tool takes over provisioning. This approach minimizes the risk of resource conflicts and gives your team time to build confidence in the new workflow. Budget for training as well -- Terraform users consistently cite learning curve as a top concern, and every alternative carries its own learning investment.