Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What Infisical states |
|---|---|
License | MIT expat license, except the ee directory, which holds premium enterprise features that require an Infisical license |
Deployment | Infisical Cloud in an EU or US region, or self-hosted with Docker or Kubernetes on any cloud, on-premises or hybrid infrastructure |
Billing unit (secrets management) | Per identity per month on Pro and Advanced; an identity is any human or machine that authenticates to Infisical |
Trial | Pro and Advanced plans include a 14-day free trial |
Security and compliance | AES-256-GCM encryption at rest and in transit; Infisical states it is SOC 2, HIPAA and FIPS 140-3 compliant |
Interfaces | Dashboard, CLI, API, SDKs for 9 languages, a Terraform provider and a Kubernetes operator |
Our take
Infisical is a strong choice if you want secrets, certificates and privileged access under one identity model, and you want the option to run it yourself. Run a proof of concept on the plan you would actually buy, because identity and approval controls are tiered.
Evaluate Infisical
Where it stands out
A free plan with no time limit. Infisical aims Free at individuals and personal projects, and it does not expire, so you can learn the workflow without a trial clock.
Short-lived credentials. Rotation runs on a schedule, with dual-phase rotations that keep the old secret until the new one has propagated; on Pro, rotation covers public databases only. Dynamic secrets, from Advanced up, issue on-demand credentials that expire or are revoked after use.
Certificates beyond issuance. The PKI side includes a dashboard with expiry warnings, continuous discovery of certificates already deployed, and certificate sync to AWS load balancers and other external systems.
Privileged access in the same platform. Users sign in with their SSO identity while Infisical brokers just-in-time access to PostgreSQL, SSH servers, Kubernetes and Active Directory, with session recording and credential rotation.
Agents work with placeholders. With Agent Vault, agent requests go through a proxy that attaches the real secret, so the agent sees only placeholders and every request is logged.
Leak prevention. The CLI scans files and git history for 140+ secret types and installs a pre-commit hook. Honey tokens alert you when a planted decoy credential is used.
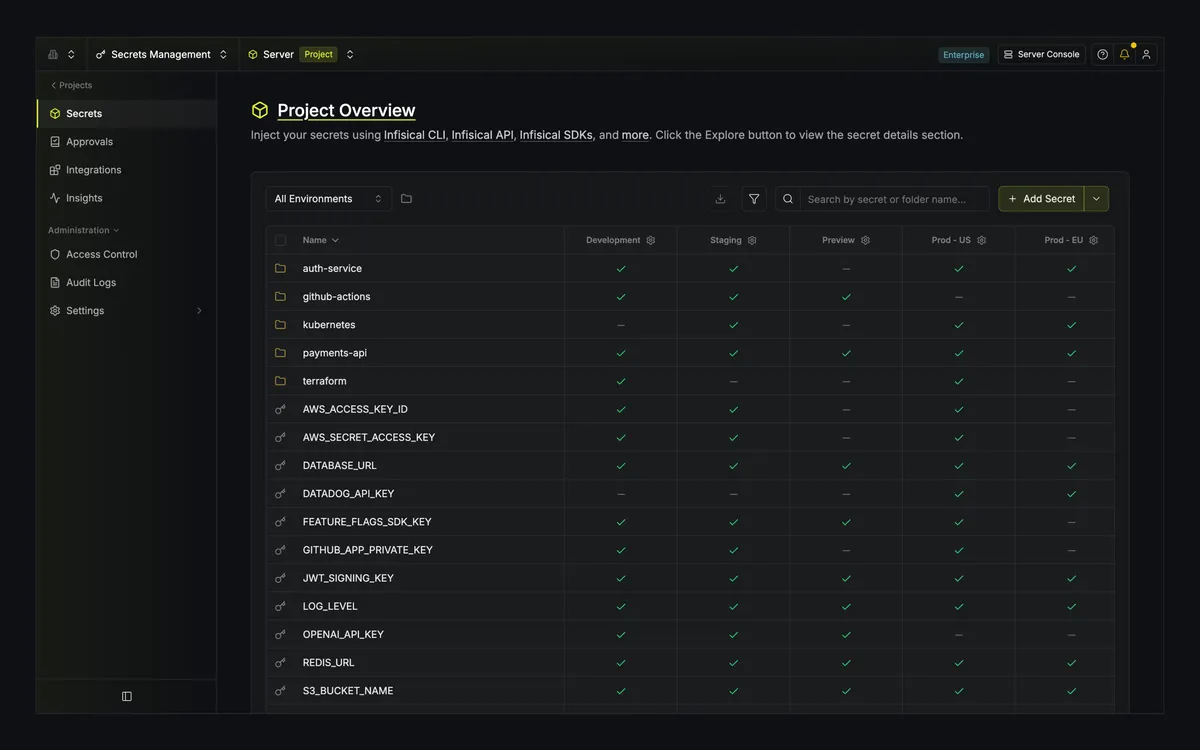
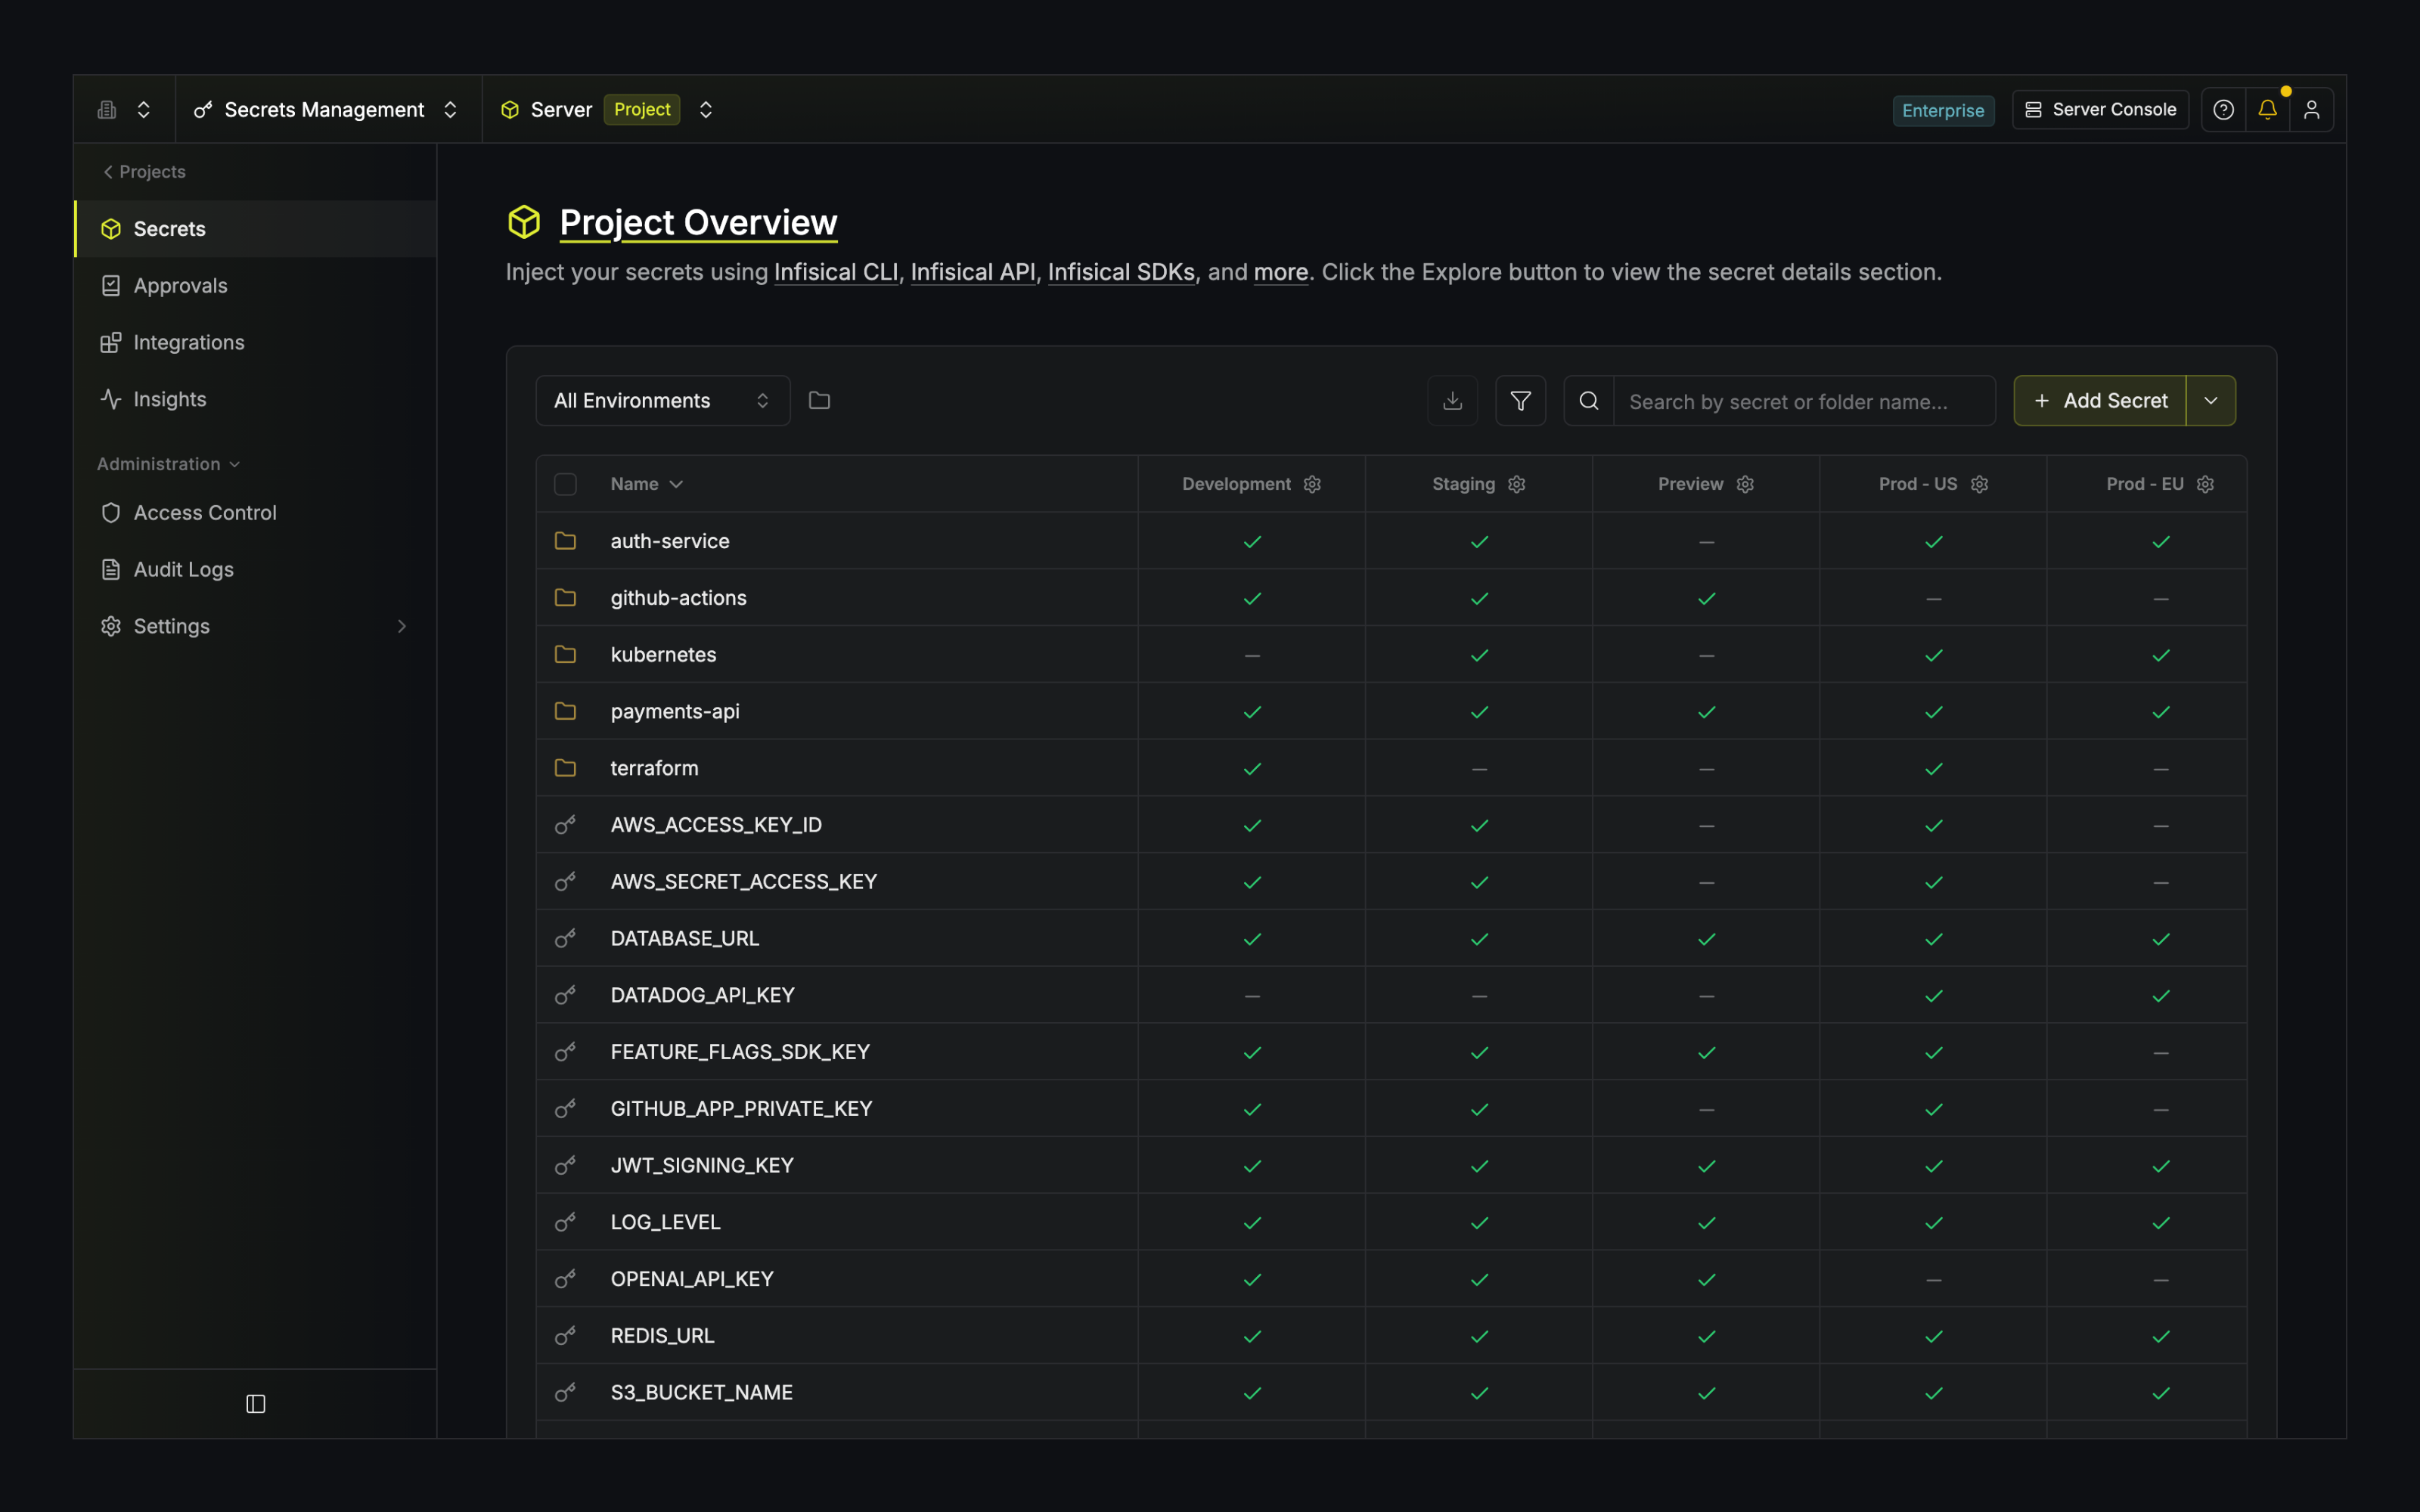
Product screenshot
Trade-offs to weigh
Machines count toward the bill. Apps, CI pipelines and services that authenticate are identities too, and each one is billed like a person on Pro and Advanced. Count machine identities before you compare with a per-seat tool.
Identity and approval controls are tiered. On the secrets management plans, SAML SSO starts on Pro, SSO and MFA enforcement on Advanced, and LDAP, SCIM, user groups, and approval workflows and access requests only on Enterprise. An organisation that requires these for secrets management should price Enterprise from the start.
Self-hosting is free only for the open-source part. Premium enterprise features sit in the ee directory and need an Infisical license, and the Enterprise plan is where self-hosting or dedicated infrastructure is listed.
Each product line has its own plans and billing unit. Secrets management is priced per identity, privileged access per user per month, and code-signing certificates case by case, so price each line you need separately.
Pricing and plan conditions
These are the secrets management plans. Projects are unlimited from the Free plan up, so adding projects does not move you to a higher plan. Each paid plan includes everything in the plan before it.
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Plan | Published price | What it adds |
|---|---|---|
Free | $0 forever | 5 identities, unlimited projects, 3 environments, 100+ integrations, secret sharing, secret references and imports, secret overrides, 2FA |
Pro | $20/identity/month billed annually (the page shows $23 without the 13% annual saving) | Everything in Free, plus unlimited identities, 6 environments per project, access controls, secret rotation (public databases only), SAML SSO, 30-day audit log retention, secret versioning, point-in-time recovery, honey tokens |
Advanced | $40/identity/month billed annually (the page shows $46 without the annual saving) | Everything in Pro, plus 12 environments per project, dynamic secrets, SOC 2 Type II, higher rate limits, custom roles, SSO & MFA enforcement, 90-day audit log retention, temporary access |
Enterprise | Custom, billed annually | Everything in Advanced, plus approval workflows & access requests, LDAP, SCIM, custom audit log retention and rate limits, user groups, 99.99% SLA, external KMS & HSM support, audit log streaming (SIEM), sub-organizations, self-hosting or dedicated infrastructure; KMIP is an add-on |
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
5.2k GitHub commits 90d30.4k GitHub stars0 vulnerabilities across 1 package
See all signals from 4 sources
PyPI · infisicalsdk@1.3.0
Alternatives to Infisical
The reviewed substitutes for Infisical among the secrets management, and what would make each one the better answer.
Direct alternatives
Reviewed substitutes: products bought for the same job, where a team picks one.
- HashiCorp Vault
- Infisical sells itself against Vault by name: the vendor publishes a Vault TCO calculator and ships migration tooling for teams moving across, and argues the case on operational cost and engineering overhead rather than on a capability Vault lacks. Both hold application secrets, both issue short-lived dynamic credentials, both do PKI, and both run self-hosted under an open licence with a managed option. A team runs one secrets platform.