Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What HashiCorp states |
|---|---|
Static secrets and storage | Vault stores arbitrary key/value pairs and can centrally store, manage, deploy and rotate static secrets on-premises or across clouds. It encrypts data before writing it to persistent storage, which can be disk, Consul and more. |
High availability | Multi-server mode runs several Vault servers, configured across availability zones or regions. Performance replication delivers a cluster to multiple regions; HashiCorp's own performance and disaster-recovery replication test examples need a Vault Enterprise binary and license. |
Multi-tenancy | Namespaces give each team an isolated environment it can self-manage, with least-privileged access. |
Access control | Authentication methods assign policies to clients; one policy framework covers identities across platforms; multi-factor authentication (MFA) is configurable. Vault records a detailed audit log. |
Developer access | One API automates secret creation, consumption, expiration and rotation. The supported Go libraries are github.com/hashicorp/vault/api and github.com/hashicorp/vault/sdk; importing github.com/hashicorp/vault itself is not a supported use. |
Our take
Choose Vault when you want short-lived, generated credentials, certificates and encryption behind one API across several clouds and on-premises systems. If you only need to keep a few static secrets, Vault is more system than the job needs.
Evaluate HashiCorp Vault
Comparisons
Where it stands out
Dynamic secrets with leases. Vault generates secrets on demand for some systems, such as AWS or SQL databases, and revokes them automatically when the lease is up. A leaked credential therefore has a limited life. The database secrets engine can also rotate passwords for existing database users.
Revocation in bulk. Vault can revoke a single secret or a tree of secrets, for example all secrets read by one user. This helps lock systems down after an intrusion.
Encryption as a service. Vault encrypts and decrypts data without storing it, so developers can keep encrypted data in a SQL database without designing their own encryption. The transit secrets engine also signs and verifies data and generates hashes and HMACs.
Certificates on demand. The PKI secrets engine generates X.509 certificates dynamically, and ACME (Automated Certificate Management Environment) manages certificate rotation.
Fits existing platforms. Vault injects secrets into Kubernetes pods, integrates with AWS IAM, and connects to CI/CD pipelines with HashiCorp Terraform, Boundary and Consul.
Customer reports. In quotes HashiCorp publishes, Canva's Anthony Ralston points to custom auth engines and secrets engines, and NORD/LB's Jannik Nolte says key management and rotation went from at least three or four full days per month to less than five minutes.
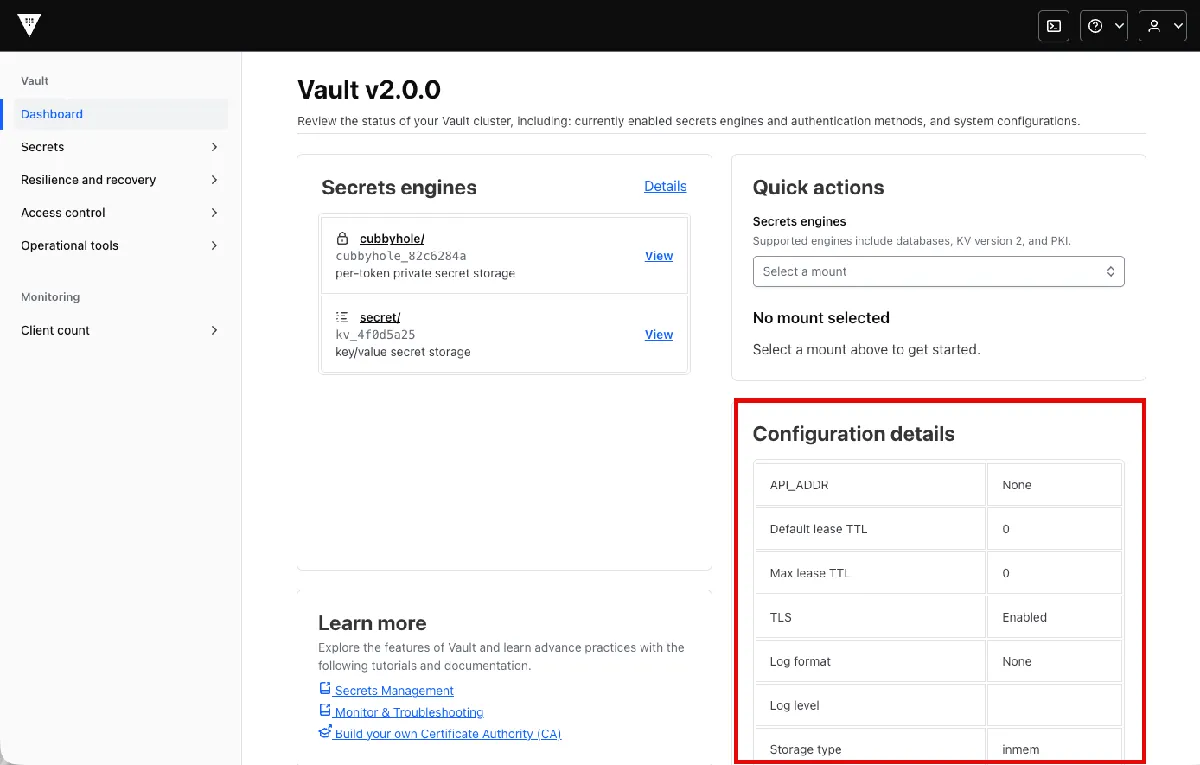
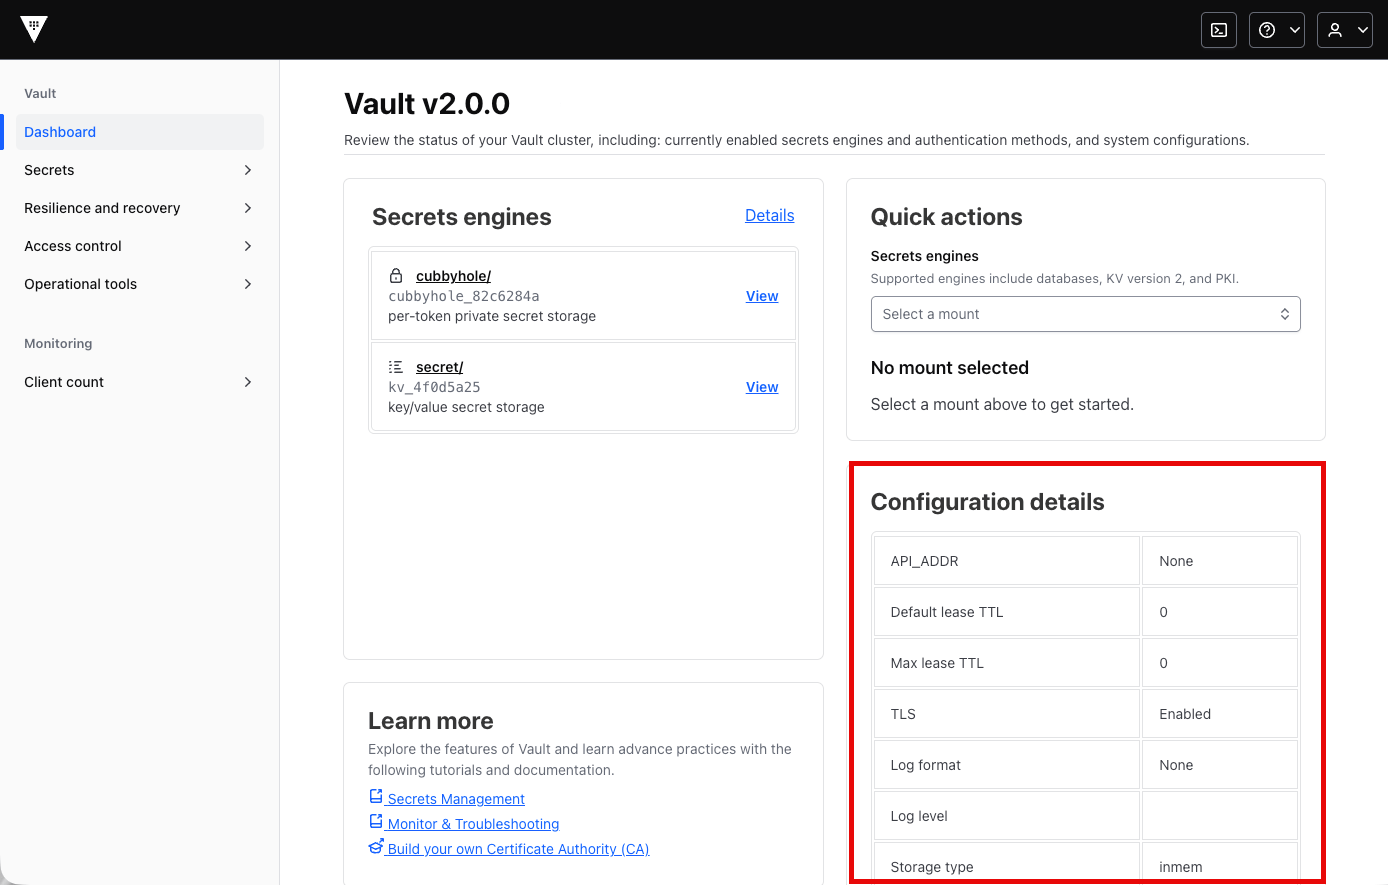
Product screenshot
Trade-offs to weigh
Self-run Vault needs an owner. You choose its storage backend and run its servers in the high-availability setup, and your applications depend on it for credentials. Plan for a team that owns it.
Many concepts to learn. Leases, revocation, authentication methods, policies, namespaces and several secrets engines each need design decisions before teams can use Vault well.
Pricing and plan conditions
HashiCorp directs buying questions to its sales team and offers demos; ask there which edition carries each feature you plan around. For a self-run build from the public repository, the bill is driven by what you supply: the servers, the storage backend and the people who operate them.
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Option | How you get it |
|---|---|
Vault (public repository) | Build it from source in the public hashicorp/vault GitHub repository |
Vault Enterprise | Runs with a Vault license; features are described on the Vault Enterprise site |
HCP Vault | Try it for free on the HashiCorp Cloud Platform |
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
917 GitHub commits 90d36.4k GitHub stars
See all signals from 5 sources
Alternatives to HashiCorp Vault
The reviewed substitutes for HashiCorp Vault among the secrets management, and what would make each one the better answer.
Direct alternatives
Reviewed substitutes: products bought for the same job, where a team picks one.
- Infisical
- Infisical sells itself against Vault by name: the vendor publishes a Vault TCO calculator and ships migration tooling for teams moving across, and argues the case on operational cost and engineering overhead rather than on a capability Vault lacks. Both hold application secrets, both issue short-lived dynamic credentials, both do PKI, and both run self-hosted under an open licence with a managed option. A team runs one secrets platform.Applies to: Holding application secrets and issuing short-lived credentials across an estate. Infisical stands in for Vault when the operational burden of running Vault is the thing being removed, or when certificate lifecycle and privileged access are wanted on the same control plane; Vault stands in when its breadth of secrets engines, existing operator expertise or tooling built on its API decide.
Related technologies
Normally used together rather than chosen between, so these are not alternatives.
- Auth0
- The two sit at different layers of one system and the documented deployments run them together, so the reader's question is which job each one does rather than which to buy.Applies to: Whether these two do the same job, or different jobs in one pipeline.