Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What the project states |
|---|---|
License | Open source under the Apache License, Version 2.0. |
Installation | Download the distribution from the Keycloak website, unzip it and run bin/kc.[sh|bat] start-dev, or run the Docker image with docker run quay.io/keycloak/keycloak start-dev. |
Scaling and availability | Clustering, which the project lists for scalability and availability. |
Application integration | The Keycloak project lists the server with Java adapters, Keycloak client libraries and a Node.js adapter (Keycloak Node.js Connect). |
Help channels | A user mailing list, the #keycloak channel on the CNCF Slack, and GitHub issues for defects; security vulnerabilities have their own reporting instructions. |
Our take
Choose Keycloak if you want one identity server, on your own infrastructure, in front of applications that use a mix of OpenID Connect and SAML, and you have people who will run it. If nobody on the team will own a login service that every application depends on, look at a hosted service instead.
Evaluate Keycloak
Where it stands out
One server for OIDC, OAuth 2.0 and SAML 2.0. Keycloak supports OpenID Connect, OAuth 2.0 and SAML, so newer and older applications can sign in through the same server.
Single sign-on and single sign-out. Users log in once to reach every connected application, and logging out once logs them out of all of them.
Keeps users where they already are. Built-in support connects to existing LDAP or Active Directory servers, so staff accounts do not need to move.
Social and partner logins without code. Social login and existing OpenID Connect or SAML 2.0 identity providers are set up in the admin console, with no code or changes to your applications.
Authorization as well as login. When role-based access is not enough, fine-grained authorization services let you define permission policies for all your services from the admin console.
Self-service for users. The account management console lets users update their profile, change passwords, set up two-factor authentication, manage sessions and view account history, which takes routine requests off administrators.
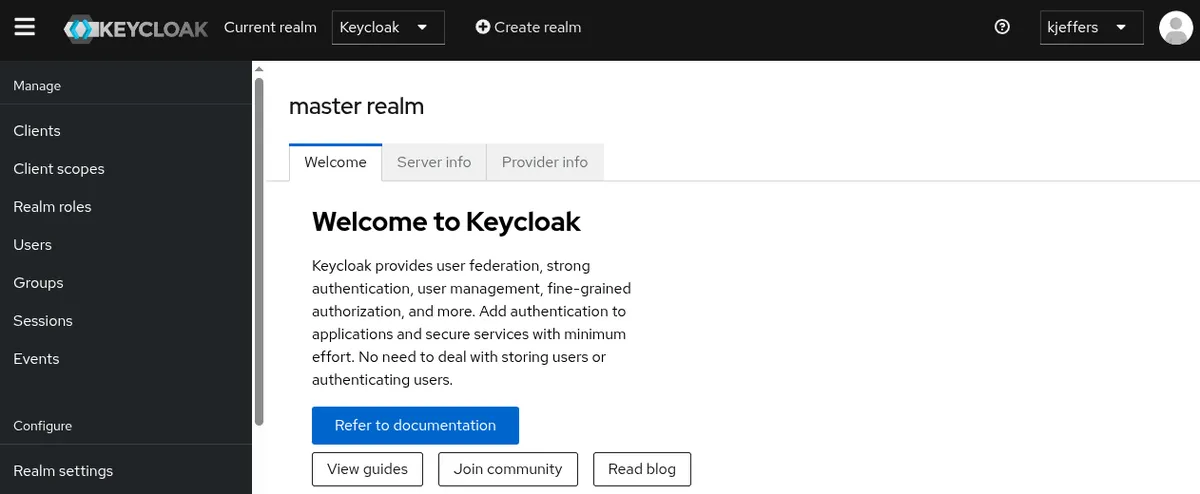
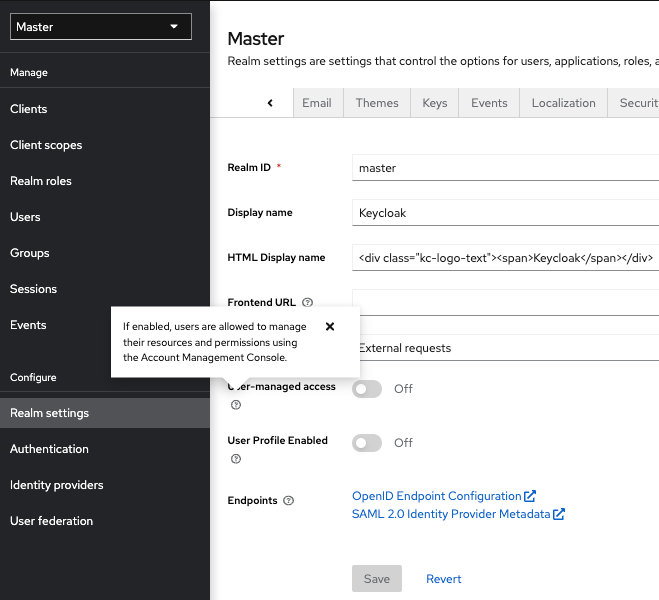
Product screenshot
Trade-offs to weigh
You operate the front door. Users authenticate with Keycloak rather than with each application, so when your Keycloak deployment is down or misconfigured, login fails across every application that depends on it. Uptime, backups and incident response sit with your team.
Upgrades are ongoing work. The project's news lists Keycloak 26.8.0 released on 01 Oct and 26.8.1 on 13 Oct; staying current means testing and rolling out releases on that kind of rhythm.
Other user stores mean code. LDAP and Active Directory are built in, but users held in other stores, such as a relational database, need a provider you implement yourself.
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
998 GitHub commits 90d37.8k GitHub stars0 vulnerabilities across 1 package
See all signals from 4 sources
npm · keycloak-js@26.2.5
Alternatives to Keycloak
The reviewed substitutes for Keycloak among the identity management, and what would make each one the better answer.
Other approaches
A different approach to the same problem. Each substitutes only for the workload named beside it.
- Auth0
- The same job — single sign-on, OIDC, OAuth 2.0 and SAML in front of every application — bought two different ways. Auth0 is hosted and billed by external monthly active user; Keycloak is Apache-2.0, a CNCF project, and run on your own infrastructure with no per-user meter at all. Conditional rather than direct because the trade is not feature-for-feature: choosing Keycloak means taking on availability, upgrades and incident response for the front door to every application, which is a capacity question before it is a product one.Applies to: Providing authentication and single sign-on across an application estate. Keycloak stands in for Auth0 when the user count makes per-MAU billing the dominant cost, or when identity data must stay on your own infrastructure; Auth0 stands in when nobody should be operating an identity server and the user count stays predictable.