Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What the project states |
|---|---|
License | Apache-2.0. |
Where it runs | Runs containers on Linux. On Mac and Windows it works through a Podman-managed virtual machine run by |
Installation | Follow the installation notes for your environment; Podman container images are on quay.io. Recent releases should run rootless without extra setup, but your operating system may need the extra configuration in the install guide, and the README says an administrator must do a little setup first. |
Release cadence and support | A major or minor release 4 times a year (second week of February, May, August and November), with patch releases at any time. All releases are PGP signed. Only the most recent release gets upstream support; an LTS version is sometimes offered as an exception. |
Help and security reports | Report security issues privately to security@lists.podman.io, not the public tracker. General questions go to Podman's channels and the lists.podman.io mailing list; bugs and features go to GitHub issues and PRs. Community meetings and Monday and Thursday office hours are free and open to everyone, hosted on Zoom through the CNCF/Linux Foundation. |
Our take
Choose Podman if you want Docker-style commands and a Docker-compatible API on hosts where you do not want a background daemon or containers running as root. It is not a runtime for the Kubernetes CRI interface; the project leaves that job to CRI-O (see Alternatives).
Evaluate Podman
Where it stands out
No manager daemon. The project says this improves security and lowers resource use at idle.
Rootless containers. A normal user can run Podman without a setuid binary. User namespaces map root in the container to that user, so a rootless container never has more privileges than the person who started it, even with
--privileged. For example, mounting the host's/etc/passwdstill does not let you change it.Docker-compatible CLI and API. The CLI can run containers locally or on remote systems. The REST API offers a Docker-compatible interface plus a second one for advanced Podman features. Podman handles OCI and Docker images, and its Usage Transfer page maps Docker commands to Podman ones.
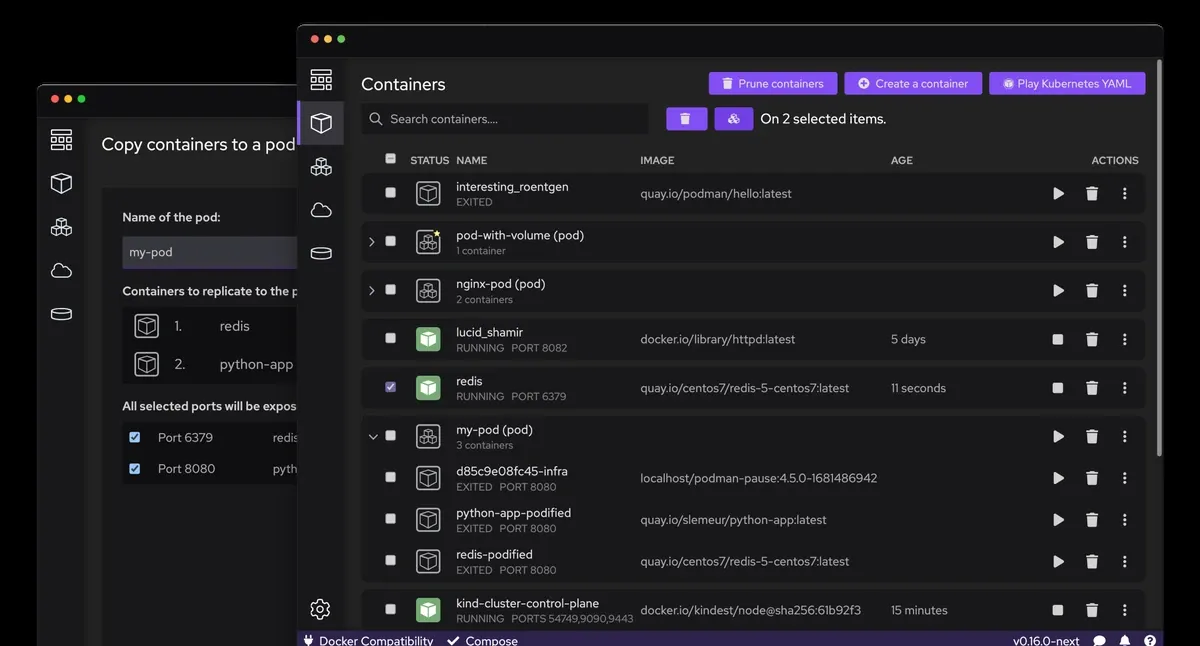
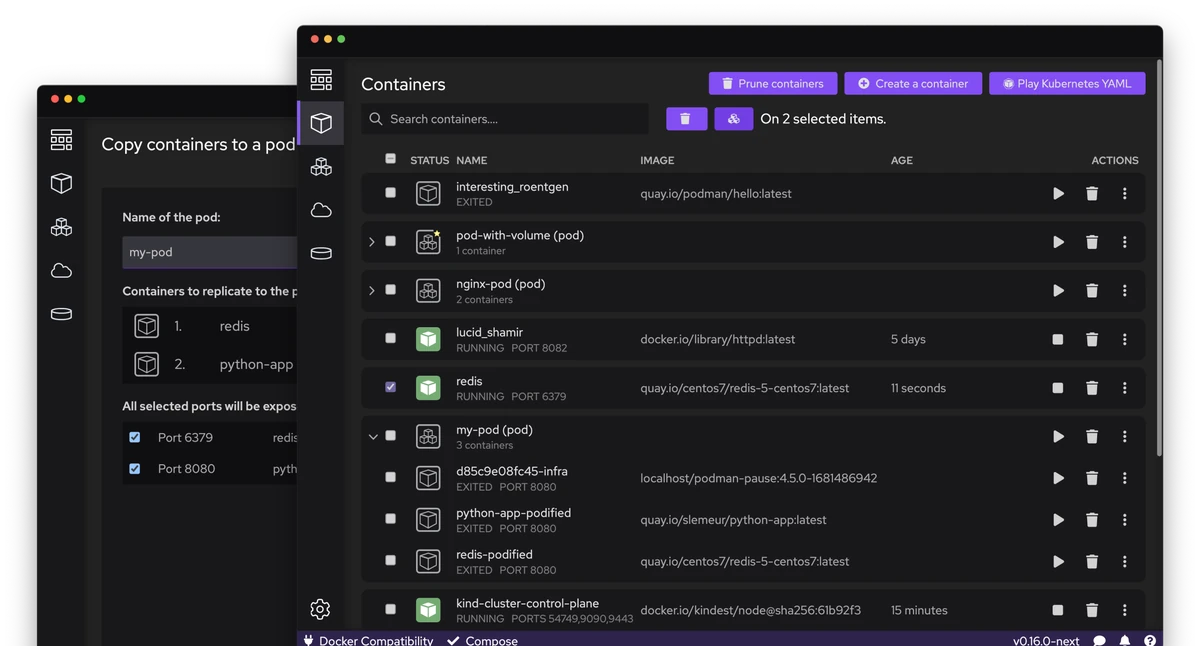
Pods and Kubernetes YAML. Pods are groups of containers that share resources and are managed together. Podman Desktop, a desktop UI for Linux, Windows and Mac, can create and manage pods and work with Kubernetes YAML.
Full lifecycle in one tool. Create containers from an image or an exploded root filesystem, checkpoint and restore them with CRIU, and pull images with trust and verification. Build from a Containerfile or Dockerfile, or commit from a container, then push to registries and other storage backends.
Standard building blocks. Builds use Buildah's golang API, but Podman installs independently of Buildah. Runtime configurations work with any OCI-compliant runtime, such as crun or runc.
Product screenshot
Trade-offs to weigh
Rootless is not complete parity. Almost all normal features work without root, but the README notes some shortcomings, and rootless networking goes through pasta. Test the networking your workload needs before you standardise on rootless.
Specialised image signing goes to Skopeo. Podman itself pushes images to registries and other storage backends, but the README puts specialised signing and pushing to various storage backends out of scope and points to Skopeo. A supply-chain pipeline with those needs will run both tools.
Laptops manage a VM too. Podman Desktop also uses the Podman backend to run containers on non-Linux systems, so Mac and Windows developers look after the virtual machine from the snapshot as well as their containers.
Plan for frequent upgrades. Given the support policy in the snapshot, teams that cannot upgrade often should arrange support elsewhere.
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
808 GitHub commits 90d33.2k GitHub stars
See all signals from 2 sources
Alternatives
Buildah. A companion project focused on building OCI images. It replicates every Dockerfile command, builds with or without a Dockerfile, needs no root and runs no daemon. Buildah containers exist only to add content to an image, while Podman containers are meant to be long lived, and neither tool can see the other's containers. Choose Buildah for scripted image builds and Podman for running containers.
CRI-O. A daemon that specialises in the Kubernetes CRI interface, which Podman leaves out of scope. It shares Conmon and a unified Seccomp policy with Podman. Choose it when Kubernetes needs a container runtime, not when people run containers by hand.
Alternatives to Podman
The reviewed substitutes for Podman among the container platforms, and what would make each one the better answer.
Direct alternatives
Reviewed substitutes: products bought for the same job, where a team picks one.
- Docker
- The same job — build and run OCI containers on a host — with a deliberate architectural split. Podman runs containers as child processes of the invoking user with no daemon, which makes rootless the default and removes the privileged socket; Docker runs a daemon and brings Docker Desktop, Compose and the body of documentation most engineers learned from. Podman's CLI is intentionally compatible, so a host runs one engine and the alias covers most everyday commands.Applies to: Building and running containers on a single host. Podman stands in for Docker when a privileged daemon is a security finding, on shared or multi-tenant hosts, or on Red Hat platforms where it is the default; Docker stands in when the surrounding tooling assumes its daemon and the daemon is not a problem.
Related technologies
Normally used together rather than chosen between, so these are not alternatives.
- Kubernetes
- Different layers of the same stack: Podman builds and runs containers on one host, Kubernetes schedules them across a cluster. Podman's pod abstraction borrows the Kubernetes model deliberately and it can generate Kubernetes manifests from a running pod, which exists to shorten the path from local development to a cluster — a pairing, not a choice.Applies to: Developing locally for a Kubernetes cluster: Podman runs the pod on a workstation and emits the manifest, Kubernetes schedules it in production.