Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What Flarehawk states |
|---|---|
Billing model | Built around Vigil investigations. Accepted uncompressed data ingest is metered separately. Never per seat. |
On every plan | SSO, SCIM provisioning, unlimited team members, notifications, security source integrations and API access. |
Currency | Prices are in USD and charged in your local currency at checkout through Stripe, where localized pricing is available. |
Getting started | Connect a telemetry source free, with no credit card and no sales call. |
Our take
Flarehawk suits a security team that is short of analyst time and wants a first pass that hands back one explained incident. Before you choose a paid plan, estimate three things: your accepted data volume, the number of Vigil investigations you expect each month, and the history you must keep. Together they decide which plan fits.
Evaluate Flarehawk
Where it stands out
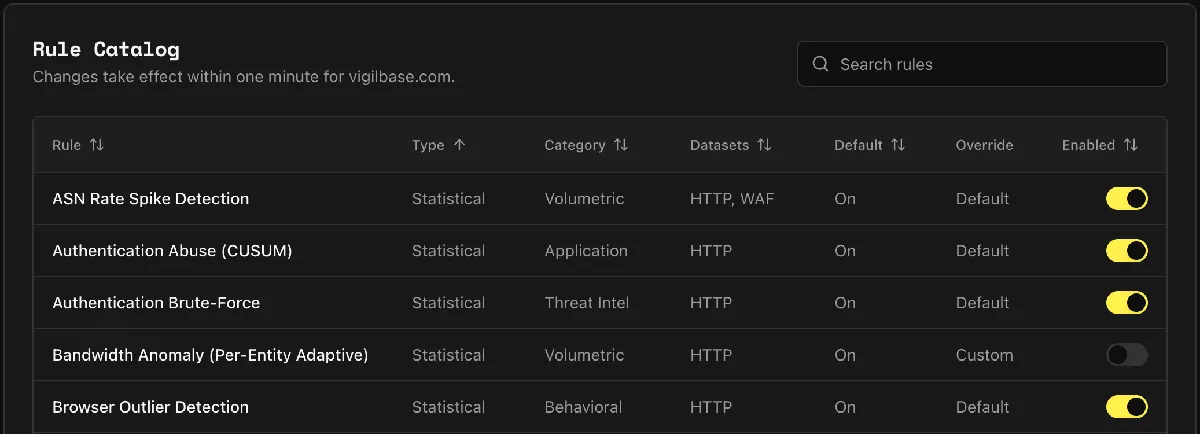
Incidents, not raw alerts. Flarehawk says it connects your security tools, groups the noise into one clear incident, explains what's at risk in plain language, and drafts a fix you can review. It acts as the first pass on your security queue, so your team spends fewer hours scanning logs.
You pay only for data that lands. Accepted data is the uncompressed size of records that pass validation and deduplication, counted only after the storage write succeeds. Rejected records and retries of an already accepted batch are never billed twice.
A free plan that cannot overrun. Free stops at a hard data cap per billing period with no overage, so a trial cannot create a bill.
A sizing guide on the pricing page. It estimates ingest from employees, monthly visitors and retention, using rough rates of ~1,500 logged requests per visit, ~300 security events per employee per day and 1.2 KB per record. Flarehawk notes that real volume depends on the sources you connect.
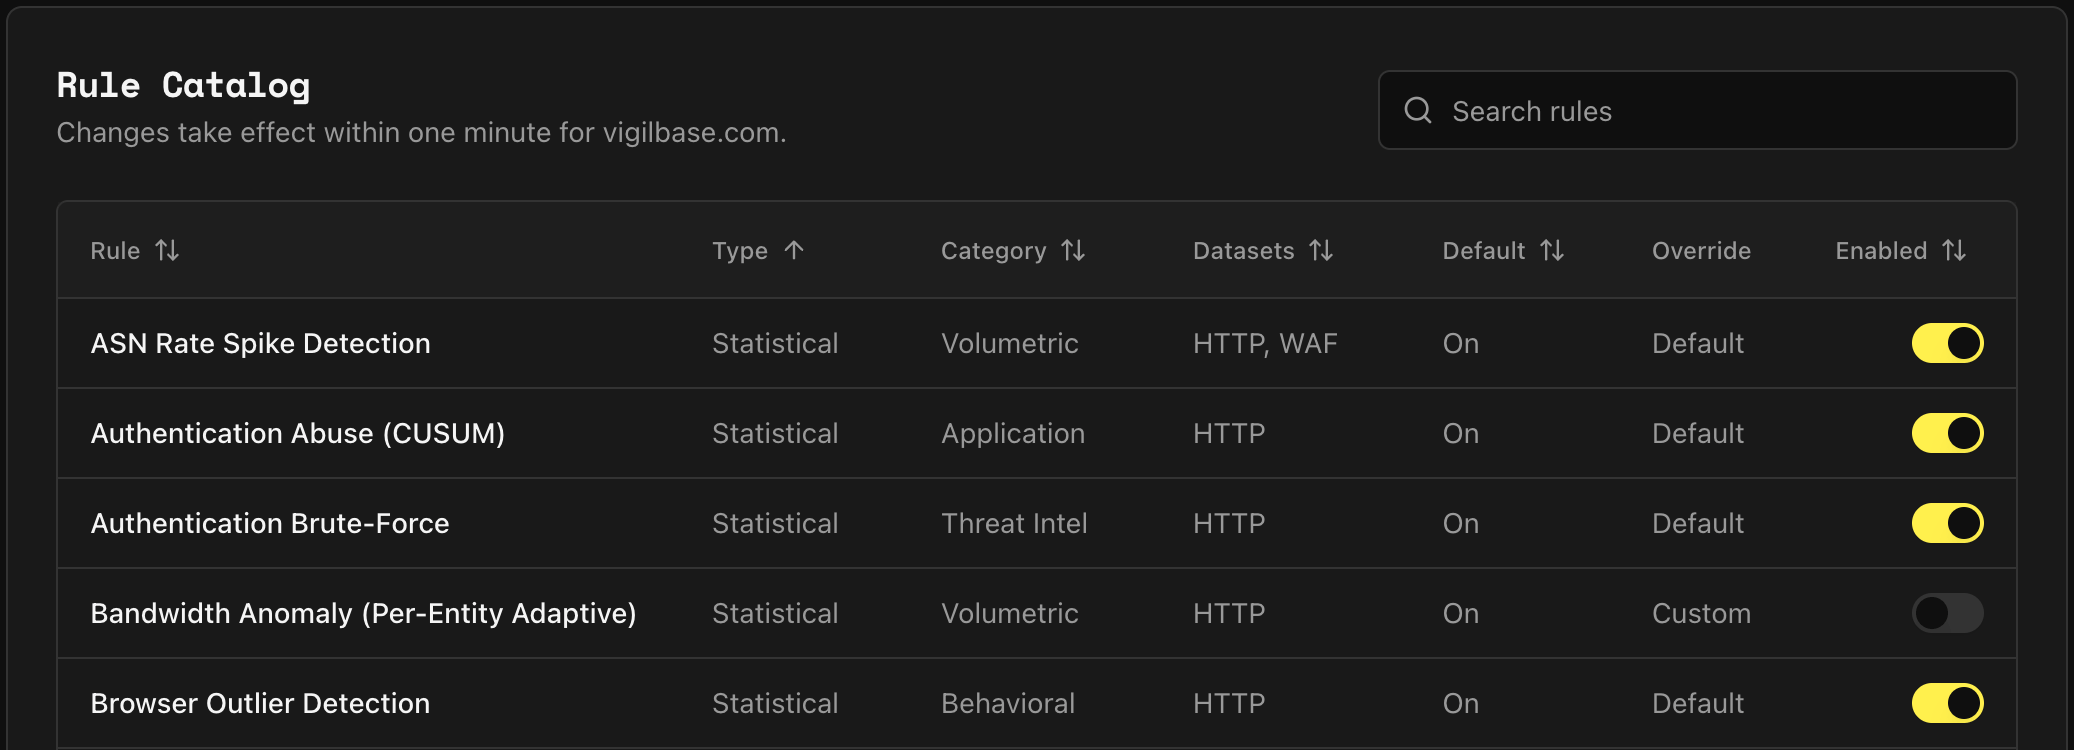
Product screenshot
Trade-offs to weigh
Size before compression. Billing counts uncompressed source size, so the compressed size of your log archives understates the volume that counts against a plan.
Volume spikes reach the bill. On Detect, Investigate and Enterprise, data above the included ingest is billed per GB, so a month with an attack or a traffic peak costs more. Only Free stops at its cap instead.
Retention is tied to the plan. If you must keep a year of history, Detect does not fit even at low volume, because its retention is shorter; Free keeps the least history of all.
A large first paid step. After Free, the next plan is Detect, a fixed monthly fee, so moving past the free trial is a budget decision.
Pricing and plan conditions
Investigations beyond a plan's allowance are listed at $10/case; on Free, investigations are a hard cap. Enterprise pricing can be customized for committed capacity and implementation requirements. If your accepted data or investigations regularly run past Detect's allowances, price Investigate as well: it includes more data, more investigations and longer retention, while overage on Detect is billed per GB and per case.
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Plan | Published price | Included each month | Data above the allowance |
|---|---|---|---|
Free | $0 | 3 Vigil investigations / month, 2 GB accepted ingest, 7 days retention | No overage; hard capped at 2 GB |
Detect | $749/mo | Ongoing detection, 10 Vigil investigations / month, 250 GB accepted ingest, 30 days retention | $4/GB above 250 GB |
Investigate | $1,499/mo | 50 Vigil investigations / month, 500 GB accepted ingest, 1 year retention | $3/GB above 500 GB |
Enterprise | Starts at $3,999/mo | 500 Vigil investigations by default, starts at 1 TB committed ingest, 1 to 5 years retention, custom invoicing and SLA | From $2.50/GB above 1 TB |
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
6 Product Hunt comments0 Product Hunt reviews
See all signals from 1 source
Alternatives to Flarehawk
Where Flarehawk sits against the products teams weigh it up with.
See detailed alternatives analysis
If you are evaluating Flarehawk alternatives, you are looking for security tools that help your team detect threats, investigate incidents, or respond to attacks across your infrastructure. Flarehawk positions itself as the autonomous control layer for security operations, ingesting Cloudflare telemetry, running AI-driven investigations, and producing remediation plans. It has a free plan with 3 investigations, 2 GB of ingest and 7-day retention. Detect costs $749/month with 10 investigations, 250 GB of ingest and 30-day retention, and Investigate costs $1,499/month with 50 investigations, 500 GB and 1-year retention. Enterprise starts at $3,999/month with 500 investigations, a 1 TB commitment and 1 to 5 years of retention. All plans include SSO, Slack integration, SQL queries, compliance exports, and API access. The alternatives below span different layers of the security stack, from phishing prevention and AI agent protection to vulnerability scanning and identity verification.
Top Alternatives Overview
DefenceNet is an AI-powered phishing protection platform built by Datacove.ai in Toronto. Rather than investigating security incidents after they occur like Flarehawk does, DefenceNet blocks malicious URLs before users click them across web, email, and SMS channels. Its ML engine analyzes SSL certificates, hosting history, and behavioral patterns in real time, delivering verdicts in milliseconds. DefenceNet offers both cloud SaaS deployment via REST API and full on-prem containerized deployment for organizations requiring data sovereignty. The runtime footprint is 50MB, and the architecture is designed for telco-scale throughput capable of handling high request volumes. DefenceNet follows an enterprise pricing model requiring direct contact for quotes. Where Flarehawk focuses on post-detection investigation and remediation, DefenceNet focuses on pre-click threat blocking.
EarlyCore provides a security layer specifically built for AI agents. It scans agents for prompt injection, data leakage, and jailbreaks before they ship, then monitors them in real time in production. EarlyCore integrates with AWS Bedrock, Google Gemini Enterprise Agent Platform (formerly Vertex AI), and custom stacks with what they describe as a 15-minute setup process. This addresses a fundamentally different security surface than Flarehawk: while Flarehawk investigates infrastructure-level security events from Cloudflare telemetry, EarlyCore protects AI-powered applications from manipulation attacks. Pricing follows an enterprise model with contact required.
Ethicore Engine Guardian SDK is a pip-installable Python threat protection layer that sits in front of any LLM provider, including OpenAI, Anthropic, and Ollama. It uses three defense layers: regex pattern matching, offline ONNX semantic embeddings, and ML behavioral inference. The SDK runs entirely offline with no cloud dependency and no latency overhead. An open-core community edition is available free on PyPI, while the licensed enterprise tier adds an expanded threat library and production models. For teams running LLM-powered features alongside Cloudflare infrastructure, Guardian SDK and Flarehawk protect complementary attack surfaces.
Vibio takes a deterministic approach to security vulnerability scanning. It runs 50+ rule-based security checks against your URL or GitHub repository, producing consistent and reproducible results on every scan. Vibio deliberately avoids AI-driven analysis to eliminate scan-to-scan inconsistency. A free plan is available; paid scans cost £4.99 for a one-time full scan, or £9.99/month for 4 scans. This contrasts with Flarehawk's ML-driven investigation model: Vibio trades adaptive intelligence for predictability, making it better suited for compliance workflows that require repeatable audit results.
PromptBrake stress-tests LLM endpoints with 138 checks across 18 attack categories, catching prompt injection, data leaks, tool misuse, and policy bypasses. It returns PASS/WARN/FAIL verdicts with evidence and remediation guidance. PromptBrake connects to any OpenAI-, Claude-, or Gemini-compatible API and exports reports for CI/CD release gates. Pricing is $499/month for its single Enterprise plan, after a free trial license of 3 scans over 7 days. Teams that run both LLM applications and Cloudflare infrastructure may use PromptBrake alongside Flarehawk to cover both AI and network security layers.
Didit v3 focuses on identity verification and fraud prevention, orchestrating KYC, biometrics, liveness detection, and AML compliance in a single platform. It uses usage-based pricing starting at $0.03 per user with 500 free checks per month and no contracts required. Didit is GDPR and ISO 27001 certified. While Flarehawk handles security operations at the infrastructure level, Didit addresses user identity fraud, making it relevant for organizations where account takeover and onboarding fraud sit alongside network threats.
Joinble AI KYC offers an Identity Intelligence OS with forensic deepfake detection, second-generation biometric verification, and AI agents for case management. It targets fintechs, crypto platforms, and marketplaces with a focus on custom verification flows without vendor dependency. Enterprise pricing requires direct contact. Joinble overlaps with Didit in the identity verification space but differentiates on deepfake detection and workflow customization.
SecureDBX handles encrypted file and secret sharing with zero-knowledge architecture. Files are encrypted in the browser before upload, with the decryption key embedded only in the share link. Four sharing modes are available: self-destructing URL links, PIN-based sharing, password-protected vaults, and text secrets for API keys. SecureDBX is open source with no account required. This addresses data-in-transit security rather than the operational threat detection Flarehawk provides.
Architecture and Approach Comparison
Flarehawk's architecture is built around a security graph called the Flarehawk Fabric, which connects requests, identities, and configuration changes from Cloudflare telemetry into a customer-specific context model. When its detection layer flags an anomaly, investigation agents spin up to analyze the event chain, produce a narrative explaining what happened, and generate a remediation plan. Every plan includes a monthly allowance of investigations: 3 on Free, 10 on Detect, 50 on Investigate and 500 on Enterprise. Log retention ranges from 7 days on Free and 30 days on Detect to 1 year on Investigate and 1 to 5 years on Enterprise. All tiers include SQL query access, compliance exports, and API access for integration with existing security workflows.
DefenceNet takes an entirely different architectural path: its ML engine runs inference on every URL and network packet in real time, analyzing behavioral patterns rather than relying on signature databases. The 50MB runtime is designed for deployment in telco-grade environments requiring high-throughput, low-latency processing. DefenceNet can run as a cloud SaaS via REST API or as a fully containerized on-prem deployment with zero external data egress, making it suitable for air-gapped networks.
EarlyCore and Ethicore Engine Guardian SDK both target AI application security but differ in deployment model. EarlyCore operates as a monitoring service for production AI agents integrated with managed cloud platforms like Bedrock and Gemini Enterprise Agent Platform. Guardian SDK runs offline as a Python library embedded directly in your application stack, using ONNX models for semantic analysis without any cloud round-trips. PromptBrake functions as an external testing harness that sends attack payloads to your LLM endpoints and evaluates security posture across 12 categories.
Vibio's architecture is deliberately stateless and deterministic. Each scan executes the same 50+ rule-based checks against a target URL or repository, producing identical results regardless of when or how often the scan runs. This makes Vibio outputs directly auditable and repeatable, a property that ML-based systems like Flarehawk or DefenceNet cannot guarantee by design.
Didit v3 and Joinble AI KYC both orchestrate multiple verification services (OCR, facial recognition, liveness, AML screening) through a single API layer, but they serve the identity verification domain rather than infrastructure security.
Pricing Comparison
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Tool | Free Tier | Paid Plans | Pricing Model |
|---|---|---|---|
| Flarehawk | Yes (3 investigations, 2 GB, 7 days) | $749/month Detect (250 GB), $1,499/month Investigate (500 GB), Enterprise from $3,999/month | Subscription + overage |
| DefenceNet | No | Enterprise (contact sales) | Enterprise |
| EarlyCore | No | Enterprise (contact sales) | Enterprise |
| Ethicore Engine Guardian SDK | Yes (open-core on PyPI) | Enterprise license (contact sales) | Open-core |
| Vibio | Yes | £4.99 per scan; £9.99/month for 4 scans | One-time or subscription |
| PromptBrake | No | $499/month, single plan | Subscription |
| Didit v3 | 500 checks/month | From $0.03/user (usage-based) | Usage-based |
| Joinble AI KYC | No | Enterprise (contact sales) | Enterprise |
| SecureDBX | Yes (open source) | Enterprise (contact sales) | Open source |
Flarehawk's Detect plan includes 250 GB of ingest with overage at $4 per GB, Investigate includes 500 GB at $3 per GB, and Enterprise starts with a 1 TB commitment and overage from $2.50 per GB. Extra investigations cost $10 each, and every plan includes unlimited team members. Among alternatives with transparent pricing, Vibio's paid scans start at £4.99 for a one-time full scan, while PromptBrake sits at $499/month for LLM security testing. Didit v3 uses pure usage-based billing starting at $0.03 per user with no contracts, making it cost-effective for variable verification volumes.
When to Consider Switching
Evaluate Flarehawk alternatives when your security requirements extend beyond Cloudflare-centric infrastructure monitoring. Flarehawk currently integrates with Cloudflare telemetry as its primary data source, with platform expansion to other cloud providers and identity systems listed on their roadmap but not yet available. If your infrastructure runs on AWS, GCP, or Azure without Cloudflare, Flarehawk's telemetry ingestion does not cover your attack surface today.
Teams building AI-powered applications should evaluate EarlyCore, Guardian SDK, or PromptBrake for prompt injection and agent manipulation risks that Flarehawk was not designed to address. Flarehawk investigates infrastructure security events; it does not inspect AI model inputs or outputs.
Budget constraints may also trigger a switch. Flarehawk's paid plans start at $749/month for Detect, with 10 investigations a month, and Investigate costs $1,499/month for 50, a significant commitment for smaller teams. Vibio provides free vulnerability scanning, Didit v3 includes 500 free identity checks monthly, and Guardian SDK's open-core edition costs nothing on PyPI.
Organizations with phishing as their primary threat vector should look at DefenceNet, which blocks malicious URLs across email, SMS, and web channels in real time. Flarehawk investigates after detection; DefenceNet prevents the click from happening in the first place.
Migration Considerations
Flarehawk's integration surface is centered on Cloudflare Enterprise telemetry ingestion, so migration paths depend on whether your replacement tool needs to consume the same data source. If you are moving to DefenceNet for phishing prevention, the integration is fundamentally different: DefenceNet operates via REST API or on-prem deployment scanning URLs and packets, rather than ingesting log streams. There is no direct log migration path between these tools since they serve different operational models.
For teams switching to EarlyCore or Guardian SDK for AI security, the migration is additive rather than replacement. These tools protect a different attack surface (AI agents and LLM endpoints) and typically run alongside infrastructure monitoring rather than replacing it. Guardian SDK installs via pip and requires no infrastructure changes, while EarlyCore connects to managed AI platforms through their existing APIs.
If you have built workflows around Flarehawk's Slack integration, SQL query interface, or compliance exports, verify that any replacement supports equivalent integration points. PromptBrake exports reports for CI/CD gates but does not offer real-time Slack alerting. Vibio provides scan results via its interface but operates as a point-in-time scanner rather than a continuous monitoring platform.
Log retention is another consideration. Flarehawk Investigate includes 1 year of log retention, Detect provides 30 days, and Enterprise offers 1 to 5 years. If you have compliance requirements for long-term log storage, ensure your replacement solution includes equivalent retention or pair it with a dedicated log management platform. Data exported from Flarehawk via its API and compliance export features should be archived before decommissioning the account.