Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What Aqua states |
|---|---|
Editions | SaaS Edition and Enterprise Self-Hosted edition. SaaS users do not deploy an Aqua server; self-hosted users deploy the Console, Gateway and Database in their own datacenter. |
Air-gapped sites | The self-hosted edition needs the CyberCenter component for air-gapped environments. |
Where components run | Kubernetes, AWS ECS, Red Hat OpenShift and hosts with no orchestrator. |
Deployment methods | Manifests, Helm charts, Operator, AWS CloudFormation, RPM (for no-orchestrator environments), scripts and the Aquactl CLI; each component supports a selection of these. |
Clouds (Cloud Security) | AWS, Azure, GCP, Oracle and Alibaba Cloud environments. |
Deployment repository license | The aquasecurity/deployments repository, which holds deployment options and aquactl configuration, is Apache-2.0 licensed. This covers the deployment files, not the commercial platform. |
Our take
Aqua makes sense if you need to block unwanted behaviour in running workloads, not only find issues, and you can deploy its enforcers on the hosts, clusters and serverless functions you want to protect. If your need is limited to CI/CD and code checks, scope a Dev Security quote first; Cloud Security is the product that adds runtime protection.
Evaluate Aqua Security
Comparisons
Where it stands out
Runtime enforcement, not just alerts. Cloud Security includes eBPF-based real-time detection, drift prevention to keep workloads immutable at runtime, and malware blocking and deletion. Aqua says its agents enforce protection locally, even when environments are disconnected or air gapped.
An enforcer for each workload type. Aqua Enforcer covers containers, KubeEnforcer covers Kubernetes workloads, VM Enforcer covers hosts and nodes, MicroEnforcer covers Containers-as-a-Service such as AWS Fargate and Azure Container Instances, and NanoEnforcer covers AWS Lambda functions.
Build-side checks in Dev Security. It lists container image scanning, Dynamic Threat Analysis (DTA) in a secure sandbox to detect sophisticated malware, Infrastructure-as-Code scanning, static pipeline analysis and automated SBOM generation.
Posture and compliance on Cloud Security. It runs hundreds of configuration checks across compute, database, storage and identity resources, with out-of-the-box compliance reporting, plus event audit trails and response policies.
Wide environment reach. Aqua names on-prem, hybrid, multi-cloud and mainframe environments, including IBM Z mainframes, and integrations across CI/CD, registries and SIEM tools.
Product screenshot
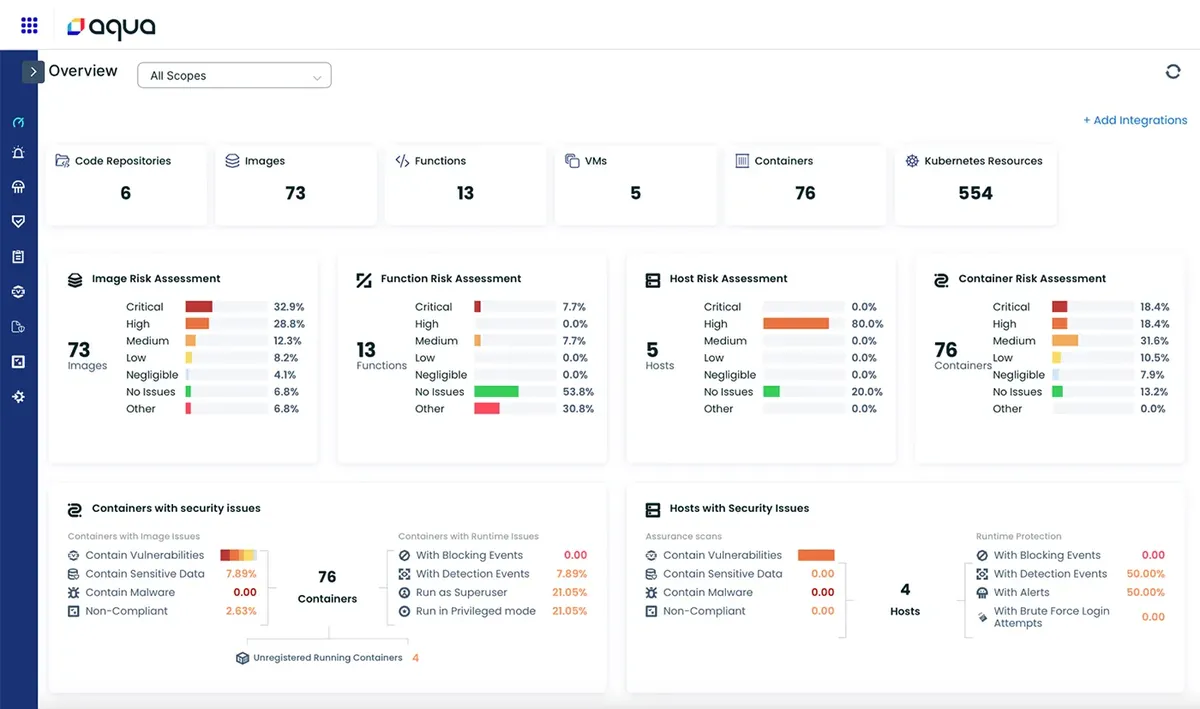

Trade-offs to weigh
Budgeting starts with a demo. The pricing page explains what each product is billed on, and its route for enterprise buyers is Get Demo, so plan for a sales conversation before you have a figure to compare.
Workload counts can move. Cloud Security bills per workload, and Lambda functions and Fargate containers are among the workloads it names. If your estate scales them up and down, ask Aqua how it counts them before you compare quotes.
Several parts to deploy. Even on SaaS you deploy enforcers and scanners; self-hosted adds the server, and some integrations such as on-premises ServiceNow and Splunk may still need the Cloud Connector. Aqua strongly recommends reading its Enforcer and deployment documentation first.
Pricing and plan conditions
The split follows where the risk sits. Pipeline, code and image checks fall under Dev Security, so its cost tracks your repositories; cloud posture and runtime protection fall under Cloud Security, so its cost tracks what you run in production. Buying both means sizing two different counts. RBAC, contextualized risk scoring and third-party integrations are available across the platform.
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Product | Billing basis | What it covers |
|---|---|---|
Dev Security | Based on the number of code repositories | Software supply chain security for the CI/CD pipeline: code repo discovery and scanning, open source health scoring, CI/CD posture management, code integrity checks, and CI/CD, registry and SCM toolchain governance. |
Cloud Security | Based on the number of workloads, such as AWS EC2 instances, Fargate containers, Lambda functions | Agentless and agent-based visibility for public cloud and K8s, CSPM, and runtime protection for cloud workloads (CWPP), including auto-discovery and agentless workload scanning. |
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
12 GitHub commits 90d64 GitHub stars
See all signals from 3 sources
Alternatives to Aqua Security
The reviewed substitutes for Aqua Security among the cloud security platforms, and what would make each one the better answer.
Direct alternatives
Reviewed substitutes: products bought for the same job, where a team picks one.
- Prisma Cloud
- Aqua Security and Prisma Cloud are cloud-native security platforms that protect containers, Kubernetes, serverless and VM workloads across the application lifecycle. Aqua Security grew from container and Kubernetes runtime protection, while Prisma Cloud, from Palo Alto Networks, bundles posture management, workload protection, identity entitlements and code security in one platform.Applies to: Choosing the platform that will assess and monitor cloud security posture.
Other approaches
A different approach to the same problem. Each substitutes only for the workload named beside it.
- Wiz
- Aqua Security is chosen instead of Wiz for cloud-native workload protection across containers, Kubernetes, serverless, and VMs. We recommend Aqua Security over Wiz for teams whose evaluation is dominated by container, Kubernetes, serverless, and VM workload protection with repository- and workload-based commercial licensing.
- Lacework FortiCNAPP
- Aqua Security is chosen instead of Lacework FortiCNAPP for cloud-native application lifecycle security workloads. We recommend Aqua Security over Lacework FortiCNAPP for teams that need lifecycle-oriented protection across containers, serverless functions, VMs, and heterogeneous deployment environments.
- Orca Security
- Aqua Security replaces Orca Security for cloud-native workload protection programs centered on containers, Kubernetes, serverless functions, and VMs. We recommend Aqua when container, Kubernetes, serverless, and workload-focused security are the center of the program.