Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What Immuta states |
|---|---|
Deployment | SaaS (the documentation is "Immuta Documentation - SaaS"); Immuta must be connected to your data platform before you can create policies |
Where rules apply | Native across warehouses, lakehouses, databases, cloud storage, APIs and SaaS |
Product structure | Four modules on one policy engine: Policy Authoring & Enforcement, Request Workflows & Exceptions, Agentic Access and Comply. Immuta says to "adopt one, add the rest" |
Developer access | Immuta CLI and API; a Terraform provider in the immuta GitHub organization wraps the Immuta V1 API |
Certifications and frameworks | SOC 2 Type II (audited annually), ISO 27001, FedRAMP Moderate (authorized for US federal agencies); supports HIPAA, GDPR and PCI DSS environments |
How to start | "Request a demo"; Immuta proposes one working session with your AI, data and security leaders to pick the first deployment point |
Our take
Shortlist Immuta if your access rules have to hold across several data systems and you must show auditors who saw which data, and why. Its design pays off when one rule replaces many per-system grants. If you run one platform and few access requests, check first whether that platform's own controls are enough before taking on a separate policy layer.
Evaluate Immuta
Comparisons
Where it stands out
Write a rule once. In the Policy Authoring & Enforcement module, you write a rule once and Immuta compiles it into the real controls inside your data infrastructure, so one rule covers every connected system. Immuta reports that Stellantis reduced 18,588 legacy permissions to 6 Immuta policies.
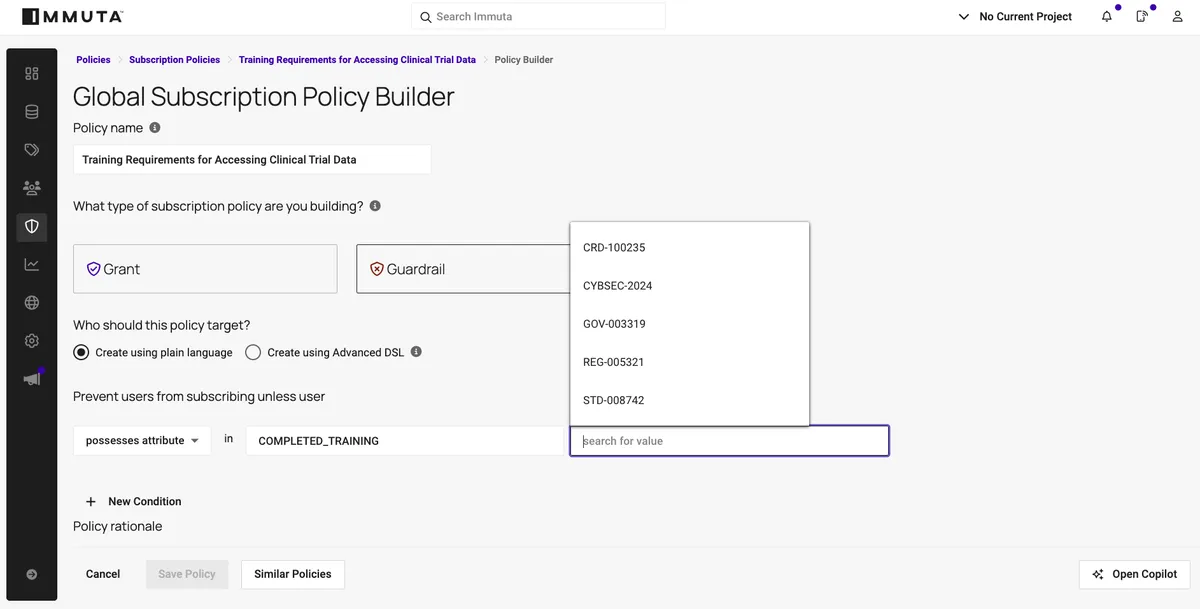
Masking and purpose rules without code. The policy builder offers Mask, Limit usage to purpose(s), Minimize and Restrict actions. A Mask rule can target columns by tag, with masking types such as NULL, hashing, constant and regex. Exceptions can apply to members of a group or users with an attribute, so access follows user and data attributes rather than one-off grants.
Time-bound exceptions. In the Request Workflows & Exceptions module, policy answers routine requests and a person decides the real exceptions. In Immuta's example, a masking exception is approved for 1 week and expires in 7 days, recorded with the reason.
Scoped access for AI agents. Each agent is a first-class identity acting for a named person. In Immuta's example, the agent gets a credential with a TTL for only the sources the task needs ("never more than the human"), and delegation to a sub-agent "can only narrow, never widen".
Audit you can query. The Comply module records every access decision as it happens. Immuta says compliance then "becomes a question you ask", for example which agents touched sensitive data this week.
Vendor-reported results at scale. Immuta reports that JPMorgan consolidated access controls for 150,000 global users in one policy layer, General Motors automated 10M+ access grants (provisioning from 5 days to 2 minutes), and Booking standardized 40,000 Snowflake and S3 tables. These are Immuta's own figures.
Product screenshot

Trade-offs to weigh
Automation depends on tagging and setup. Before policies run on their own, Immuta's setup steps have you connect your data platform, add metadata and users, and organize data into domains. Automated policies use tags, which come from data catalogs you already use or from Immuta's identification. Budget time for this groundwork.
Terraform provider needs local builds. The README says to build the provider with make and install it as a local plugin through a filesystem mirror. It lists a known limitation: terraform destroy "seems to do nothing when tested with user attributes". Teams that manage access as code should test it first.
New platform framing. Immuta's homepage marks the Immuta Data Authorization Platform as new and lists further manifesto parts for December and January. Ask which modules your contract covers, since Immuta lets you adopt modules one at a time.
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
0 GitHub commits 90d0 GitHub stars
See all signals from 3 sources
Alternatives to Immuta
The reviewed substitutes for Immuta among the data access control, and what would make each one the better answer.
Other approaches
A different approach to the same problem. Each substitutes only for the workload named beside it.
- Collibra
- A catalog documents and governs assets; a policy engine enforces access at query time. Catalogs have added policy features and policy engines have added metadata, so the decision is whether enforcement needs its own system or the catalog's controls are enough.Applies to: Whether access policy is enforced by the catalog or by a dedicated policy engine.
- Atlan
- A catalog documents and governs assets; a policy engine enforces access at query time. Catalogs have added policy features and policy engines have added metadata, so the decision is whether enforcement needs its own system or the catalog's controls are enough.Applies to: Whether access policy is enforced by the catalog or by a dedicated policy engine.
- Alation
- A catalog documents and governs assets; a policy engine enforces access at query time. Catalogs have added policy features and policy engines have added metadata, so the decision is whether enforcement needs its own system or the catalog's controls are enough.Applies to: Whether access policy is enforced by the catalog or by a dedicated policy engine.
See detailed alternatives analysis
If you are evaluating Immuta alternatives, you are likely looking for a platform that addresses data access governance, data quality monitoring, or data cataloging with a different approach to pricing, integration depth, or operational focus. Immuta occupies a distinctive niche as a data provisioning and access control platform that enforces policies natively across cloud data platforms like Snowflake, Databricks, and BigQuery. Below, we break down the leading alternatives and help you determine which solution fits your data stack and governance requirements.
Top Alternatives Overview
We have identified ten strong alternatives to Immuta, spanning data governance platforms, data observability tools, and data catalog solutions.
Collibra is an enterprise data governance platform recognized as a Leader in the Gartner Magic Quadrant for Data and Analytics Governance Platforms. It delivers a unified view across data cataloging, quality observability, lineage, and AI governance. Collibra holds an 8/10 rating based on 18 reviews, and serves organizations that need broad governance capabilities rather than deep access control at the compute layer.
Anomalo takes an AI-first approach to data quality, using unsupervised machine learning to detect anomalies across structured, semi-structured, and unstructured data without requiring manual rule configuration. It is backed by both Databricks Ventures and Snowflake Ventures, and connects directly to cloud warehouses for automated monitoring.
Bigeye positions itself as an Enterprise AI Trust Platform, combining data observability with cross-source column-level lineage, sensitive data discovery, and AI governance modules. It is built for large enterprises that need to monitor data pipelines while also enforcing data access policies for AI applications.
Atlan provides a modern data workspace combining cataloging, governance, and real-time collaboration. Atlan publishes no prices; every plan is quoted by sales.
Select Star is an automated data discovery platform that builds catalogs, lineage maps, and semantic models from your existing data. Select Star is now part of Snowflake and publishes no plans or prices.
Soda is an AI-native data quality platform focused on catching data incidents before they reach production. It provides a free tier alongside its Team plan at $750/month, with enterprise features available at custom pricing.
Metaplane serves as a data observability platform with a free plan, a usage-based Pro plan and a quoted Enterprise plan. It monitors data pipelines, alerts on breakages, and provides metadata context for debugging.
Datafold is a data observability platform that helps prevent data issues proactively. It offers a self-hosted deployment alongside its managed cloud, both quoted per deployment.
Castor (CastorDoc) is an automated data discovery and catalog tool that provides a single source of truth for data documentation and discovery, featuring a search-driven interface designed to make data findable across the organization.
Validio provides automated data observability and quality monitoring designed to make enterprise data AI-ready, focusing on identifying and resolving data issues before they create business impact.
Architecture and Approach Comparison
Immuta operates at the data access layer, enforcing policies natively within your cloud data platforms. Rather than copying or moving data, Immuta applies attribute-based access control (ABAC), role-based access control (RBAC), and purpose-based policies directly at query time across Snowflake, Databricks, BigQuery, Starburst/Trino, PostgreSQL, and numerous other platforms. Its architecture centers on three pillars: policy authoring (with plain-language support), automated provisioning of data access requests, and continuous monitoring through unified audit logs. Immuta also supports conversational AI capabilities for managing data access at scale and integrates with identity stores like Active Directory, Okta, and SAML providers.
Collibra takes a broader governance-first approach, providing a unified platform for data cataloging, quality observation, compliance reporting, and AI use case governance. Where Immuta focuses on enforcing access at the compute layer, Collibra excels at organizing metadata, establishing business glossaries, building data lineage views, and managing privacy risk. Collibra also provides AI governance capabilities for cataloging, assessing, and monitoring AI use cases.
Anomalo and Bigeye both approach the problem from the data observability angle but differ architecturally. Anomalo uses a proprietary data profiling and prediction engine with unsupervised ML models that learn historical patterns in each table and flag deviations automatically, without requiring manual threshold setting or rule creation. Bigeye builds on cross-source column-level lineage to enable dependency-driven monitoring, connecting anomaly detection to upstream root cause identification and downstream impact analysis. Anomalo excels at zero-configuration anomaly detection, while Bigeye provides stronger lineage-based debugging workflows.
Atlan and Select Star represent the data catalog and discovery approach. Both automate metadata management, but Atlan emphasizes real-time collaboration and AI-driven data search, while Select Star focuses on automated lineage generation and semantic model building from actual data usage patterns.
Soda, Metaplane, Datafold, and Validio all focus on data quality monitoring. Soda provides AI-native automated detection and resolution. Metaplane positions itself as the monitoring layer for modern data stacks. Datafold emphasizes proactive prevention through data diffing and testing. Validio targets continuous monitoring to keep enterprise data AI-ready.
The fundamental architectural difference is that Immuta sits between users and data platforms as a policy enforcement layer, while most alternatives either sit alongside your data stack as observability or cataloging tools, or above it as governance orchestration platforms.
Pricing Comparison
Immuta operates on an enterprise pricing model where you need to contact their sales team for specific quotes. Most direct governance competitors follow a similar approach.
Collibra, Anomalo, Bigeye, Castor, and Validio all use enterprise pricing models that require contacting sales for a quote. This is common among platforms targeting large organizations with complex data environments.
Atlan and Select Star also publish no prices. Metaplane has a free plan, a usage-based Pro plan and a quoted Enterprise plan. Soda provides a free tier alongside its Team plan at $750/month. Datafold offers a self-hosted deployment alongside its managed cloud, both quoted per deployment.
When comparing pricing, keep in mind that Immuta is a policy enforcement platform that may reduce the need for manual access management, request ticketing, and compliance audit effort. The total cost of ownership should factor in whether your organization can consolidate multiple point solutions or whether you need specialized tools at each layer of your data stack.
When to Consider Switching
There are several scenarios where exploring Immuta alternatives makes practical sense for your organization.
If your primary challenge is data quality monitoring rather than access control, platforms like Anomalo, Soda, or Metaplane will address your needs more directly. Immuta does not focus on anomaly detection or data quality scoring -- it assumes your data pipelines deliver quality data and focuses on governing who can access it and under what conditions.
If you need a comprehensive data catalog and governance platform with strong metadata management, business glossaries, and compliance reporting, Collibra or Atlan provide that breadth. While Immuta integrates with external catalogs including Alation, Atlan, and Collibra, it does not replace their cataloging functionality.
If you are a smaller team or early-stage company looking for affordable data tooling, the freemium options from Atlan, Select Star, Metaplane, or Soda provide lower-friction entry points compared to Immuta's enterprise sales process. You can start monitoring data quality or building a catalog without a procurement cycle.
If your organization needs deep data lineage and impact analysis to understand how data flows through your entire stack, Bigeye or Select Star offer lineage-centric capabilities that extend beyond Immuta's access control focus. Understanding upstream causes and downstream effects of data issues requires a different architectural approach than policy enforcement.
If you are primarily working with a single cloud data platform, evaluate whether that platform's native governance features (such as Snowflake's access policies or Databricks Unity Catalog) meet your access control requirements before investing in a standalone tool.
Migration Considerations
Migrating away from Immuta requires careful planning because it operates at the policy enforcement layer of your data stack. Any access control policies, data masking rules, and provisioning workflows currently managed through Immuta will need to be replicated or replaced in the new environment.
Start by auditing your existing Immuta policy library. Document all ABAC, RBAC, and purpose-based policies, along with any dynamic masking rules and the data platforms they apply to. Export Immuta's unified audit logs before decommissioning to preserve your compliance trail. Immuta supports pushing audit data into external systems, so leverage this capability during the transition.
Next, inventory your integration points. Immuta connects with identity stores (Active Directory, Okta, SAML, LDAP), data catalogs (Alation, Atlan, Snowflake Horizon, Databricks Unity Catalog, Collibra), and business applications. Each of these integrations will need equivalent connections in your replacement solution or direct configuration within your cloud platforms.
Consider the approval workflow impact. Immuta automates data access request routing and provisioning, including time-bound access and conditional approvals. If your teams rely on these workflows, ensure your replacement platform supports similar request-and-approve patterns, or plan to build these workflows using ticketing and orchestration tools.
For teams adding observability tools like Anomalo, Soda, or Bigeye alongside or instead of Immuta, the migration is simpler because these tools operate at a different layer of the stack. They connect directly to your data warehouse and can begin monitoring without disrupting existing access controls.
We recommend a phased approach where both systems run in parallel during the transition. Because Immuta enforces policies at query time, removing it prematurely could expose sensitive data. Validate that replacement policies are correctly enforced before decommissioning Immuta's policy layer.