Buying snapshot
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Decision point | What Grafana Labs states |
|---|---|
License | Distributed under AGPL-3.0-only, with Apache-2.0 exceptions listed by Grafana Labs. |
Ways to run it | Three options: open-source Loki that you set up and maintain yourself; Grafana Cloud Logs, a fully managed service based on Loki; and Enterprise Logs, a self-managed edition with expert support from Grafana Labs, offered by demo request. |
What is indexed | A set of labels for each log stream, not the log text. Compressed, unstructured logs are stored as they arrive. |
Storage | Persists 100% of data to object storage. |
Stack around it | Alloy collects and sends logs, Loki stores and queries them, and Grafana displays them. Queries use LogQL, from Grafana or the LogCLI command line. |
Multi-tenancy | Built in. To run several tenants locally, the README sets auth_enabled to true and adds a runtime config with tenant-specific overrides. |
Open-source help | Community forum, the #loki channel in Grafana Slack, GitHub issues and a project mailing list. |
Our take
Choose Loki if your team already labels workloads the Prometheus way and wants logs on the same labels, in object storage. Self-host it if you can run and upgrade a log system yourself; otherwise start on Grafana Cloud Logs, where the free tier lets you test the label model on real traffic before paying.
Evaluate Grafana Loki
Where it stands out
One set of labels for metrics and logs. Loki groups streams by the labels teams already use with Prometheus, so you can move from a metric to the matching logs. For Kubernetes, Pod labels are scraped and indexed automatically.
Small index by design. Grafana Labs says that indexing only metadata makes Loki simpler to operate and cheaper to run, and that log lines can be queried within milliseconds of arrival.
No format rules at ingest. Logs can arrive in any format from many clients, and you parse them at query time.
Alerts and metrics from log lines. Loki can evaluate alerting rules on incoming logs and send the alerts to a Prometheus Alertmanager for routing.
Starts as one binary. Loki can run on a single host with no dependencies, and Grafana Labs also designed it to run as microservices when you need to scale out.
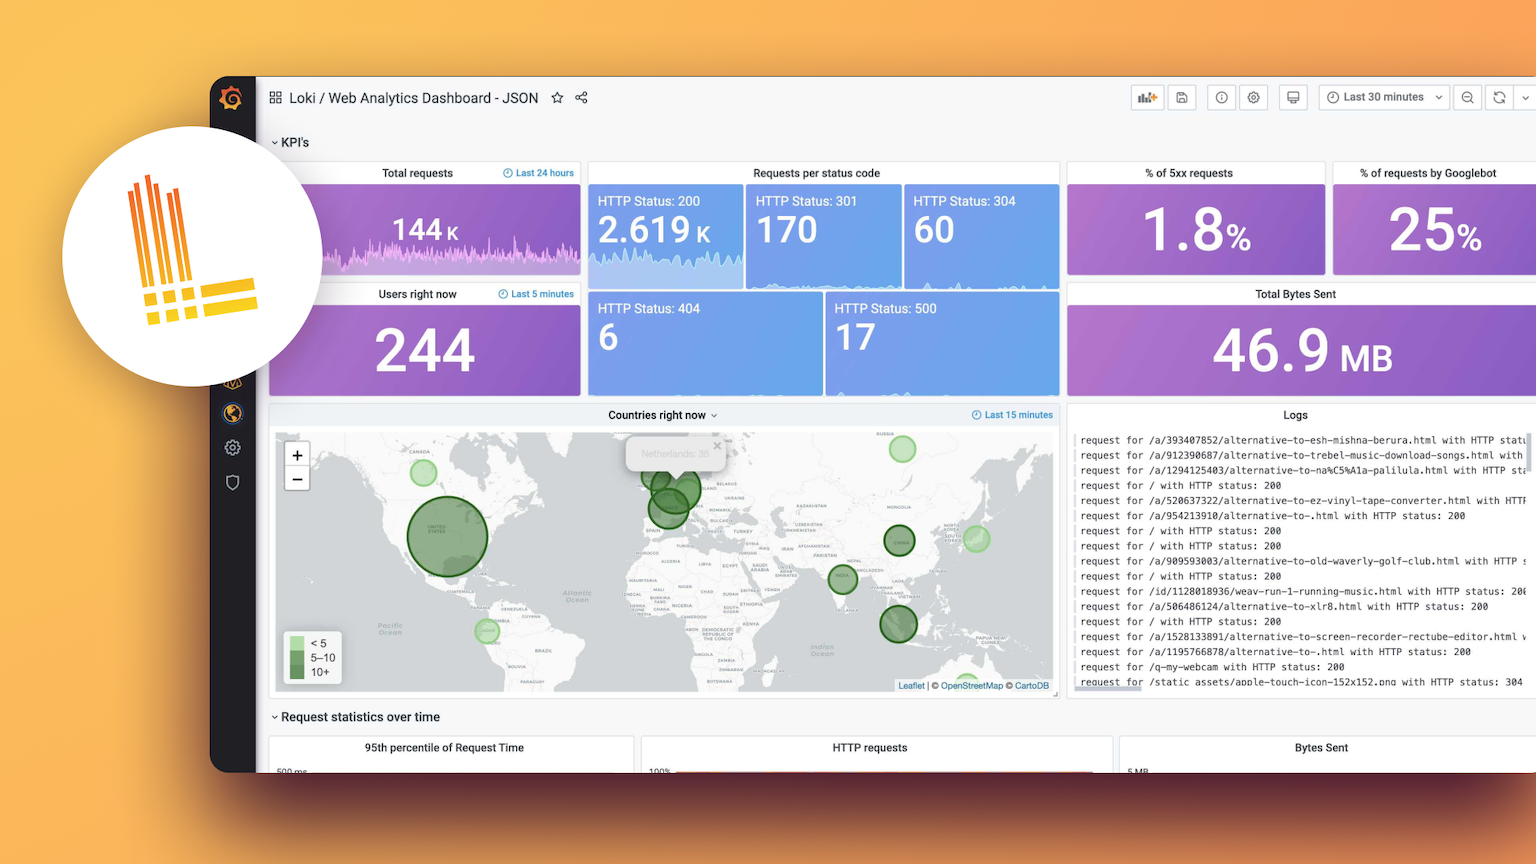
Product screenshot
Trade-offs to weigh
Label design decides how you search. Loki does no full-text indexing, so queries first select streams by label and then read the stored log text. Plan your labels before you send production volume.
The Helm chart moved. Effective March 16, 2026, the Loki Helm chart was forked to grafana-community/helm-charts; the chart in the Loki repository is maintained for Enterprise Logs (GEL) users only. Self-hosted Kubernetes installs should track the community chart.
Collection agent has changed. Alloy replaced Promtail in the Loki stack: Promtail is considered feature complete, and future log-collection development will be in Grafana Alloy.
AGPL terms apply to the open-source build. Teams that change or redistribute Loki should check the AGPL-3.0-only license and Grafana's Apache-2.0 exceptions with their legal team.
Pricing and plan conditions
Open-source Loki is licensed under AGPL-3.0-only; with it you run and pay for your own servers and object storage. Grafana Cloud Logs on the Pro plan is billed per GB on three separate meters (process, write and retain) after the first 50 GB ingested each month, on top of the plan's monthly platform fee. Logs is one of several Grafana Cloud services on the same account, each with its own usage meter. Grafana Labs says pricing is volume-based and tiered, and offers an interactive calculator.
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Plan | Published price | What it adds for logs |
|---|---|---|
Free | $0 | Logs limited to 50 GB ingested per month with 14 day retention; all Grafana Cloud services with usage limits; community support; no credit card required. |
Pro | From $19 / month + usage. Logs: $0.050/GB Process, $0.400/GB Write, $0.100/GB Retain | Everything in Free plus: 50 GB ingested per month, then pay as you go; 30 days retention for logs; 8x5 email support. |
Enterprise | Starts at $25,000 / year spend commit. Logs: custom, scalable unit price based on annual commit | Premium support, custom retention and deployment flexibility (Public Cloud, Federal Cloud, or Bring Your Own Cloud), discussed with sales. |
Cloud Logs includes Adaptive Logs, which finds common log patterns and recommends which unused telemetry to drop. Grafana Labs says it can cut log ingest by up to 50%.
Public signals
About these signals
Verified factual signals from public sources. They indicate observable activity or interest, not total adoption, product quality, or cost.
1.4k GitHub commits 90d29.1k GitHub stars
See all signals from 5 sources
Alternatives to Grafana Loki
The reviewed substitutes for Grafana Loki among the log management, and what would make each one the better answer.
Other approaches
A different approach to the same problem. Each substitutes only for the workload named beside it.
- Elastic Observability
- Choose Elastic Observability when you want Elasticsearch's query model without self-hosting Elasticsearch.Applies to: Logs with search as the primary access pattern. Elastic Observability stands in for Loki when full-text search over log bodies is how engineers work and a managed platform is wanted; Loki stands in when queries are label-scoped and storage cost decides.
- Datadog
- Choose Datadog when UX and correlation matter more than cost.Applies to: Choosing a log destination alongside existing telemetry. Datadog stands in for Loki when APM is already there and incident correlation across traces, metrics and logs is the job; Loki stands in for a Prometheus and Grafana shop that wants to keep ingest cost down and run its own store.
- Dynatrace
- Loki keeps the log bodies out of the index and in object storage, which is what makes it cheap at volume and what makes full-text search slower. The fork here is whether logs live in a dedicated store or inside a platform that already holds the rest of the telemetry. Dynatrace is named with Datadog as the enterprise-grade choice for complex multi-cloud estates where budget is secondary to capability, which is the opposite of the constraint Loki is designed for.Applies to: Logs for a complex multi-cloud estate. Dynatrace stands in for Loki when automated analysis across a large heterogeneous estate is worth the price; Loki stands in when ingest volume drives the bill and the team already runs Prometheus and Grafana.
- Splunk
- Choose Splunk when security teams own your log stack and budget allows.Applies to: Deciding where application logs go. Splunk stands in for Loki when the logs are evidence -- security investigation, compliance retention, a search language analysts already know; Loki stands in when the logs are for debugging and the bill scales with volume.
- Amazon CloudWatch
- Choose CloudWatch when your workload is entirely AWS-based and you want zero-config log collection from AWS services.Applies to: Logs for workloads running on AWS. CloudWatch stands in for Loki when the estate is AWS-only and zero integration work matters most; Loki stands in when volume makes per-GB ingest pricing the dominant cost, or the estate spans clouds.
- Azure Monitor
- The fork is the cloud's default against a best-of-breed store. Logs land in the provider's own service with no integration work and a bill that grows with ingest and retention; Loki costs a cluster to run and keeps bodies in object storage, which is why it stays cheap at volume. Azure Monitor is the same bargain inside Azure: the platform's own logs arrive there already.Applies to: Logs for workloads running on Azure. Azure Monitor stands in for Loki when the estate is Azure-only; Loki stands in when ingest volume drives the bill or the team wants one log store across clouds.
- New Relic
- Choose New Relic when you want a single commercial vendor for the full observability stack and per-host pricing fits your workload.Applies to: Deciding whether logs belong in the observability platform or a separate store. New Relic stands in for Loki when one platform for all telemetry is the goal; Loki stands in when logs are the high-volume signal and cost is the constraint.
- Observe
- Observe sells a single managed platform that ingests logs alongside the rest of the telemetry and charges for the service; Loki is a component a team runs itself inside a Grafana stack. Same trade as the other managed observability pairs: operations and correlation bought with subscription cost, against cost control bought with operational work.Applies to: Choosing between a managed observability platform and a self-run log store. Observe stands in for Loki when nobody wants to operate the log tier; Loki stands in when the team already runs Prometheus and Grafana and wants the ingest bill under its own control.
- Honeycomb
- The fork is the shape of the data rather than the price of it. Honeycomb is built around wide structured events queried at high cardinality for debugging unknown-unknowns; Loki is a log store that indexes labels and keeps bodies in object storage. A team that has decided its telemetry is events rather than log lines is not shopping for a log store at all.Applies to: Investigating production behaviour. Honeycomb stands in for Loki when the team instruments wide events and queries at high cardinality; Loki stands in when the signal is ordinary log lines and the cost of keeping them is the constraint.
- SigNoz
- Choose SigNoz when you want less operational complexity than the LGTM stack while keeping the open-source, OpenTelemetry-first architecture.Applies to: Self-hosting observability. SigNoz stands in for Loki when the team wants one open-source product covering traces, metrics and logs; Loki stands in when Prometheus and Grafana are already the stack and only the log tier is missing.
- Elasticsearch
- Choose Elasticsearch when query speed on ad-hoc full-text searches over large time ranges matters more than storage cost.Applies to: Storing and searching logs. Elasticsearch stands in for Loki when engineers need fast full-text search across unstructured log bodies; Loki stands in when queries are label-scoped and storage cost at volume decides.
Related technologies
Normally used together rather than chosen between, so these are not alternatives.
- Grafana
- Loki is the log store in the Grafana stack and Grafana is the interface you read it through; the reviewers' line is that if you are already on Prometheus and Grafana, Loki is the natural fit. A team runs both, so presenting one as an alternative to the other would be wrong in the plain sense of the word.Applies to: A Grafana-based observability stack: Grafana renders the dashboards and queries, Loki stores the logs behind them.
See detailed alternatives analysis
Looking for Grafana Loki alternatives? Loki is the open-source log aggregation system from Grafana Labs, free under AGPL v3 for self-hosting and available via Grafana Cloud or Grafana Enterprise Logs for managed deployments. It dominates Kubernetes-native log aggregation thanks to cheap storage costs (typically 5-10x cheaper than Elasticsearch at scale) and tight Prometheus-style integration. Teams evaluate alternatives when Loki's label-discipline requirements become a problem, when they need faster full-text search than Loki's two-phase query model provides, or when they lack Kubernetes expertise to run it. Below, nine log management and observability platforms worth evaluating — with honest trade-offs, DB-verified pricing, and clear guidance on when each one is the better choice.
Top Alternatives Overview
Elasticsearch is Loki's biggest architectural contrast — full-text indexing (every field indexed) versus Loki's label-only indexing. Self-hosted Elasticsearch is free but operationally heavy; commercial Elastic Cloud Hosted starts at $99/month (Standard). Choose Elasticsearch when query speed on ad-hoc full-text searches over large time ranges matters more than storage cost. It wins on search flexibility; Loki wins on cost efficiency at scale.
Splunk is the gold standard for SIEM, compliance, and enterprise log analytics. Splunk Community Edition is free (single-user, self-hosted); Splunk Enterprise uses custom pricing, historically among the most expensive in observability. SPL (Splunk's query language) is more powerful than LogQL for complex security workflows. Choose Splunk when security teams own your log stack and budget allows.
Grafana Cloud includes managed Loki plus Grafana plus Tempo plus Mimir. Freemium with vendor-quoted enterprise pricing. It's the natural upgrade path if you want Loki's model without running it yourself — Grafana Cloud's free tier covers small workloads, paid tiers scale with usage. Choose Grafana Cloud when your team lacks Kubernetes expertise but you still want the LGTM architecture.
Datadog offers polished SaaS log management as a separately priced product (Logs is a separate SKU), alongside infrastructure monitoring at $15 per host per month billed annually. Datadog Logs has excellent search UX and cross-correlation with metrics, traces, and errors. Much more expensive than self-hosted Loki but dramatically easier to operate. Choose Datadog when UX and correlation matter more than cost.
Amazon CloudWatch is AWS-native, with a free tier and per-unit usage billing from $0.50 per GB of metric ingestion. CloudWatch Logs works well for AWS-native workloads and integrates cleanly with AWS services, but lacks Loki's Kubernetes-native ergonomics. Logs Insights query language is functional but less expressive than LogQL. Choose CloudWatch when your workload is entirely AWS-based and you want zero-config log collection from AWS services.
SigNoz consolidates what Loki + Grafana + Tempo + Mimir does into a single application. Self-hosted free (Apache 2.0); SigNoz Cloud at $0.30 per GB ingested. Choose SigNoz when you want less operational complexity than the LGTM stack while keeping the open-source, OpenTelemetry-first architecture. SigNoz trades some Grafana dashboard polish for architectural simplicity.
New Relic offers full APM with integrated log management; Standard is $10 for the first full platform user and $99 per additional user, plus $0.40 per GB of data. New Relic Logs is bundled with the broader observability platform — you get logs as one data type alongside metrics, traces, and errors. Choose New Relic when you want a single commercial vendor for the full observability stack and per-host pricing fits your workload.
Elastic Observability is the managed Elasticsearch play specifically for observability use cases — Standard from $99/month, Platinum from $131/month, Enterprise from $184/month on Elastic Cloud Hosted. It's the managed version of the Elasticsearch-vs-Loki trade-off. Choose Elastic Observability when you want Elasticsearch's query model without self-hosting Elasticsearch.
Prometheus is Loki's metrics counterpart in the Grafana LGTM stack — free, open source, CNCF standard. Prometheus and Loki share the same service-discovery model and label conventions, which is why they're typically deployed together. Prometheus doesn't handle logs, so it's not a direct Loki replacement, but teams moving off Loki often keep Prometheus for metrics alongside whatever they replace Loki with.
Architecture and Approach Comparison
These platforms split into three camps. Loki, SigNoz, and the Prometheus-plus-friends stack use label-based or OpenTelemetry-native indexing models — cheap storage, disciplined cardinality management required, and query models inherited from Prometheus. Elasticsearch, Elastic Observability, and Splunk use full-text indexing — expensive storage, fast ad-hoc search, query languages designed for log analytics (Query DSL, SPL). Datadog, New Relic, and CloudWatch are commercial SaaS platforms where log management is one feature among many — you pay for convenience and polish rather than choosing an architectural model. Loki's distinctive choice is the label-only index: it keeps costs down at scale but requires cardinality discipline that teams without platform engineering often mishandle. Practical implication: switching between label-based platforms (Loki ↔ SigNoz) is an agent-and-endpoint change; switching from label-based to full-text (Loki → Elasticsearch) requires rethinking how you query logs.
Pricing Comparison
Scroll sideways to see all columns. With a keyboard, focus this table and use the arrow keys.
| Tool | Free Tier | Paid Plans (starting) | Focus Area / Key Differentiator |
|---|---|---|---|
| Grafana Loki | Yes — self-hosted free under AGPL v3 | Grafana Cloud free tier; Enterprise Logs custom | Cheap-storage log aggregation with LogQL |
| Elasticsearch | Yes — self-hosted free (Apache 2.0 / ELv2) | Elastic Cloud from $99/month | Full-text indexing with query flexibility |
| Splunk | Community Edition free (self-hosted) | Splunk Enterprise custom pricing | SIEM-grade log analytics with SPL |
| Grafana Cloud | Yes (free tier, ~50 GB/month) | Vendor-quoted for enterprise | Managed LGTM stack (Loki + Grafana + Tempo + Mimir) |
| Datadog | Yes | Infrastructure Pro $15 per host per month (annual) + usage add-ons | Breadth + polish; multi-cloud default |
| Amazon CloudWatch | Yes | Free tier, then per-unit usage from $0.50/GB | AWS-native logs and metrics |
| SigNoz | Yes — self-hosted free; Cloud 10 GB/month | Cloud from $0.30 per GB | Unified logs/metrics/traces in one app |
| New Relic | Yes | Standard from $10 for the first full platform user, $99 per additional user + $0.40/GB | Full APM with integrated logs |
| Elastic Observability | No | From $99 / $131 / $184 per month (Standard / Platinum / Enterprise) | Managed Elasticsearch for observability |
| Prometheus | Yes (100% open source) | Free | Metrics-only; companion to Loki |
When to Consider Switching
Label cardinality explosions are breaking Loki operationally — if developers keep adding high-cardinality labels (user IDs, request IDs) and your platform team can't enforce discipline, switch to a full-text indexed tool (Elasticsearch, Splunk) where cardinality doesn't break query performance. You need faster ad-hoc full-text search — Loki's two-phase query model is slow when label filters don't narrow the search enough. Elasticsearch and Splunk are meaningfully faster for "grep across 30 days" queries. Your team doesn't have Kubernetes expertise to run the LGTM stack — Grafana Cloud's managed Loki or SigNoz Cloud remove this operational burden. SIEM and compliance workflows are dominant — Splunk and Elasticsearch have much stronger SIEM app ecosystems than LogQL. You want a unified observability experience — SigNoz, Datadog, or New Relic consolidate logs with metrics and traces in a single product rather than Loki's multi-component stack.
Migration Considerations
Loki-to-alternative migrations are non-trivial because the underlying storage models differ significantly. Moving to Elasticsearch requires re-indexing historical data (Loki's chunked storage doesn't port to Elasticsearch's inverted index) — most teams start fresh in the new platform and keep Loki read-only for 3-6 months while historical context ages out. Moving to Splunk is similar: parallel ingestion for 2-4 weeks, validate queries against real workloads, then cut over. Moving to Grafana Cloud's managed Loki is the smoothest path — your existing Loki data can be imported and LogQL queries work unchanged. Moving to SigNoz requires instrumentation changes since SigNoz is OpenTelemetry-first rather than Promtail/Grafana-agent-first. Plan for dashboard rebuilds in all cases — Loki dashboards typically don't translate automatically to other platforms. Critical: don't migrate during peak season; observability gaps during cutover are expensive. Budget platform-engineering time for validating alarm parity, especially for alerts that rely on LogQL's specific semantics. Finally, confirm data-retention parity — Loki's cheap object-storage retention is often more cost-effective than alternative platforms' retention pricing, which may constrain how much history you can afford to keep in the new tool.