Decision comparison
Wiz vs Snyk
Wiz and Snyk address fundamentally different security domains. Wiz is the definitive choice for cloud infrastructure security, providing CNAPP capabilities including CSPM, CWPP, CIEM, and runtime threat detection across multi-cloud environments. Snyk leads in developer-first application security, excelling at SCA, SAST, and IaC scanning within developer workflows. Many enterprises deploy both tools together to achieve full code-to-cloud security coverage.
Architecture choice. These take different approaches to the same problem. Read the table as a fit question rather than a feature race.
These are different kinds of product — Cloud Security Platform and Code Security.
Quick Comparison
| Decision factor | Wiz | Snyk |
|---|---|---|
| Best For | Cloud security posture management, runtime threat detection, and infrastructure-level risk reduction | Developer-first application security including SCA, SAST, container scanning, and IaC testing |
| Security Scope | CNAPP covering cloud infrastructure, workloads, containers, IAM, and runtime threats | AppSec platform covering open-source dependencies, custom code, containers, and IaC |
| Pricing Model | Enterprise-only pricing, custom quotes. Wiz publishes no rate and quotes every deal. Per-workload pricing model. No free tier or self-service plans. | Free: up to 200 open-source tests/month, 100 container tests/month, 300 IaC tests/month. Team: $25/developer/month (billed annually), unlimited tests, Jira integration, fix PRs. Enterprise: custom pricing, SSO, RBAC, custom policies, SLA. |
| Deployment | Agentless cloud-native scanning with optional eBPF runtime sensor | Integrates directly into IDE, CI/CD pipelines, and developer workflows |
| Ease of Use | Fast onboarding with agentless scanning; results within 60 minutes of deployment | Developer-friendly with IDE plugins, CLI tools, and automated fix pull requests |
| Community/Support | Rated #1 in cloud security with 772+ reviews on G2; trusted by 50%+ of Fortune 100 | Trusted by Okta, Revolut, and Skechers; strong developer community and integrations |
Wiz
- Best For:
- Cloud security posture management, runtime threat detection, and infrastructure-level risk reduction
- Security Scope:
- CNAPP covering cloud infrastructure, workloads, containers, IAM, and runtime threats
- Pricing Model:
- Enterprise-only pricing, custom quotes. Wiz publishes no rate and quotes every deal. Per-workload pricing model. No free tier or self-service plans.
- Deployment:
- Agentless cloud-native scanning with optional eBPF runtime sensor
- Ease of Use:
- Fast onboarding with agentless scanning; results within 60 minutes of deployment
- Community/Support:
- Rated #1 in cloud security with 772+ reviews on G2; trusted by 50%+ of Fortune 100
Snyk
- Best For:
- Developer-first application security including SCA, SAST, container scanning, and IaC testing
- Security Scope:
- AppSec platform covering open-source dependencies, custom code, containers, and IaC
- Pricing Model:
- Free: up to 200 open-source tests/month, 100 container tests/month, 300 IaC tests/month. Team: $25/developer/month (billed annually), unlimited tests, Jira integration, fix PRs. Enterprise: custom pricing, SSO, RBAC, custom policies, SLA.
- Deployment:
- Integrates directly into IDE, CI/CD pipelines, and developer workflows
- Ease of Use:
- Developer-friendly with IDE plugins, CLI tools, and automated fix pull requests
- Community/Support:
- Trusted by Okta, Revolut, and Skechers; strong developer community and integrations
Public signals
Verified factual signals only. Bars appear only for like-for-like metrics with five weekly assessments for every tool; missing evidence stays explicit. These signals do not establish enterprise adoption, product quality, or total cost.
| Metric | Wiz | Snyk |
|---|---|---|
| Search interest(Market interest) | 0 | Not available |
| Hacker News mentions, 90d(Community interest) | 0 | 6 |
| Docker Hub pulls(Product adoption) | Not available | 45.7M |
| GitHub commits, 90d(Developer adoption) | Not available | 526 |
| GitHub stars(Developer adoption) | Not available | 5,500+ |
| npm weekly downloads(Product adoption) | Not available | 515.7k |
| Stack Overflow questions(Community interest) | Not available | 105 |
As of September 14, 2026 — updated weekly.
Health & risk evidence
Observed public-source checks for mapped package versions and repositories.
Wiz
Package vulnerabilities
Not available
Repository security score
Not available
Snyk
September 14, 2026Package vulnerabilities
npm · snyk@1.1307.2
0 vulnerabilities
across 1 package
Repository security score
Not available
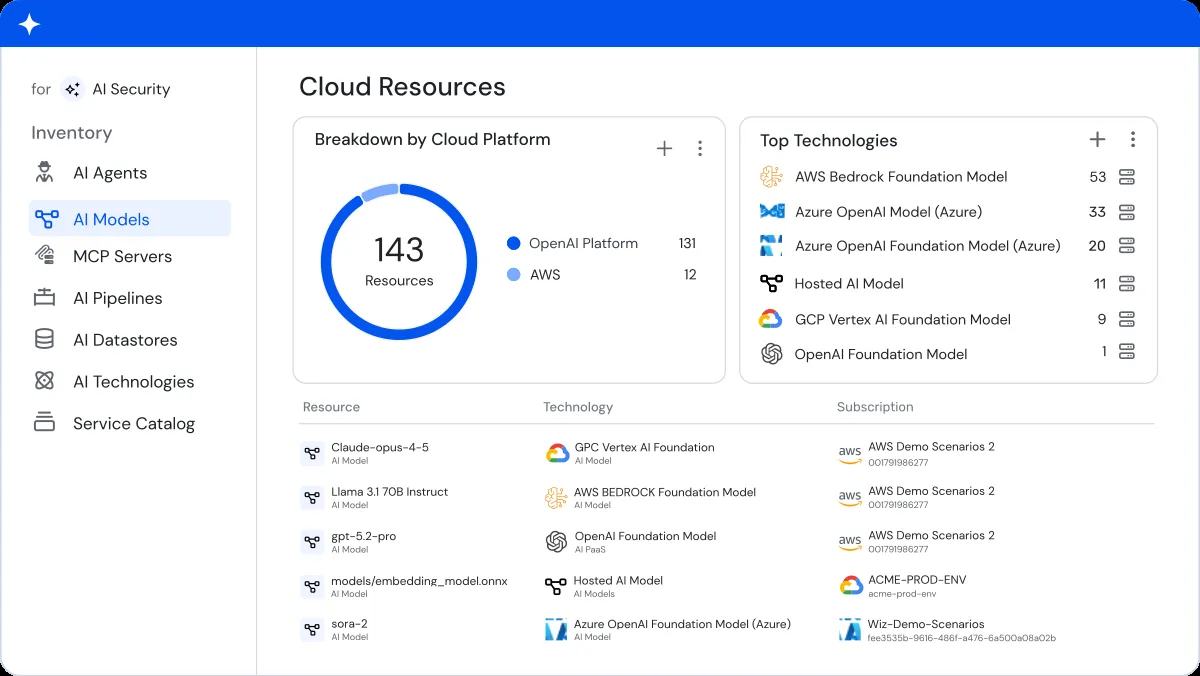
Interface Preview
Wiz
Snyk
Feature Comparison
| Feature | Wiz | Snyk |
|---|---|---|
| Security Scanning Capabilities | ||
| Open-Source Dependency Scanning (SCA) | Limited; focuses on vulnerability detection within cloud workloads rather than code-level dependencies | Core strength with vulnerability database covering 200+ languages and package managers |
| Static Application Security Testing (SAST) | Code scanning available through Wiz Code but secondary to cloud posture focus | Deep SAST engine with AI-powered analysis of first-party code vulnerabilities |
| Cloud Security Posture Management (CSPM) | Industry-leading CSPM with full cloud configuration analysis across AWS, Azure, and GCP | Not a primary focus; relies on IaC scanning to catch misconfigurations before deployment |
| Container Image Scanning | Scans running container workloads and images within cloud environments | Scans container images in registries and CI/CD pipelines with 100 free tests/month |
| Infrastructure as Code (IaC) Security | Supports IaC scanning as part of broader code-to-cloud coverage | Dedicated IaC scanning with 300 free tests/month covering Terraform, CloudFormation, and Kubernetes |
| Cloud and Runtime Protection | ||
| Runtime Threat Detection | eBPF-based runtime sensor detects and blocks active exploitation and lateral movement in real time | No runtime threat detection; focuses on pre-deployment scanning and shift-left security |
| Attack Path Analysis | Security graph models lateral movement, privilege escalation, and data access chains across cloud | Not available; security scope ends at the application and dependency layer |
| Cloud Workload Protection | Full CWPP with agentless scanning of VMs, containers, serverless, and data stores | Limited to container scanning; does not provide runtime workload protection |
| Identity and Access Analysis | CIEM capabilities analyze IAM permissions, detect over-privileged identities, and model access risks | Not available; does not analyze cloud identity or access management |
| Developer and Integration Features | ||
| IDE Integration | Available through Wiz Code for scanning in development environments | Deep IDE plugins for VS Code, IntelliJ, and others with inline fix suggestions |
| CI/CD Pipeline Integration | Integrates with CI/CD for code and IaC scanning as part of code-to-cloud pipeline | Native integrations with GitHub, GitLab, Bitbucket, Jenkins, and 30+ CI/CD tools |
| Automated Remediation | Wiz Green agent generates code fixes and opens PRs to remediate infrastructure issues at source | Automated fix PRs for vulnerable open-source dependencies with upgrade and patch recommendations |
| AI Security Features | AI-SPM discovers AI models, agents, and MCP servers; detects AI-specific runtime threats | Evo AI-SPM governs risk in AI-generated code; scans AI-native application components |
Security Scanning Capabilities
Open-Source Dependency Scanning (SCA)
Static Application Security Testing (SAST)
Cloud Security Posture Management (CSPM)
Container Image Scanning
Infrastructure as Code (IaC) Security
Cloud and Runtime Protection
Runtime Threat Detection
Attack Path Analysis
Cloud Workload Protection
Identity and Access Analysis
Developer and Integration Features
IDE Integration
CI/CD Pipeline Integration
Automated Remediation
AI Security Features
Which approach fits
Wiz and Snyk address fundamentally different security domains. Wiz is the definitive choice for cloud infrastructure security, providing CNAPP capabilities including CSPM, CWPP, CIEM, and runtime threat detection across multi-cloud environments. Snyk leads in developer-first application security, excelling at SCA, SAST, and IaC scanning within developer workflows. Many enterprises deploy both tools together to achieve full code-to-cloud security coverage.
When each approach fits
Choose Wiz if:
For securing cloud infrastructure, detecting runtime threats, analyzing attack paths, and managing cloud security posture across AWS, Azure, and GCP environments.
Choose Snyk if:
For developer-first application security including open-source dependency scanning, static code analysis, container image scanning, and IaC testing integrated into CI/CD workflows.
These scenarios reflect the available product evidence. Your requirements, existing stack, and team expertise should guide the final decision.
Frequently Asked Questions
Can Wiz and Snyk be used together?
Yes, many enterprises deploy both tools as complementary solutions. Snyk secures the application layer during development by scanning code, dependencies, containers, and IaC, while Wiz secures the cloud infrastructure layer by monitoring runtime workloads, cloud configurations, identity permissions, and active threats. Together they provide end-to-end code-to-cloud security coverage.
Which tool is better for a small development team?
The supplied Wiz pricing evidence does not provide a public starting price or a basis for comparing suitability by team size. Wiz describes its licensing as modular, scaling with workloads, active developers, log ingestion, or sensors, and its pricing page is a custom-quote request form. A buyer should confirm which modules apply, the relevant licensing metric, and the quoted terms for their environment.
Does Wiz replace the need for application security tools like Snyk?
No. Wiz primarily secures cloud infrastructure, workloads, and runtime environments. While Wiz Code provides some code scanning capabilities, it does not match Snyk's depth in open-source dependency analysis, SAST for first-party code, or developer workflow integration. Organizations with active development teams benefit from both a CNAPP like Wiz and an AppSec platform like Snyk.
What cloud providers does each tool support?
Wiz provides agentless scanning across AWS, Azure, and GCP, with deep integration into each cloud provider's services, identities, and network configurations. Snyk is cloud-agnostic at the application layer, integrating with any CI/CD pipeline or container registry regardless of the underlying cloud provider. Snyk's IaC scanning covers Terraform, CloudFormation, Azure Resource Manager, and Kubernetes manifests.
How do Wiz and Snyk differ in their approach to AI security?
Wiz's AI-SPM continuously discovers AI models, agents, MCP servers, and services across cloud and SaaS environments, identifying AI-specific risks like sensitive data exposure and detecting runtime threats from malicious agent actions. Snyk's Evo AI-SPM focuses on the code layer, helping teams see and govern risk in AI-generated code before it ships and scanning AI-native application components for vulnerabilities.